
Portfolio Tracking, Risk Assessment, and MEV Protection: Choosing the Right DeFi Workflow
Consider a familiar US DeFi situation: you open your wallet before work and discover that your portfolio appears healthier than expected. A token balance has risen, but a lending position is close to liquidation. A swap you submitted last night settled at a worse price than the quote. Meanwhile, a dashboard reports one neat total value that quietly combines volatile assets, debt, pending rewards, and illiquid positions. Nothing has necessarily been hacked. The problem is that the interface has compressed several different risks into one number.
Effective DeFi security therefore begins before a transaction is signed. It requires three connected practices: tracking what the portfolio actually contains, assessing how its exposures can change, and reducing the information leakage that allows hostile or opportunistic transaction ordering. These practices overlap, but they are not interchangeable. A wallet can simulate a transaction without providing full portfolio accounting; a portfolio tracker can show risk without protecting a pending swap from maximal extractable value, or MEV, strategies. The useful question is not which tool is “best,” but which failure mode each workflow addresses.
Why a portfolio balance is not a risk assessment
Portfolio tracking is usually treated as an accounting problem: identify wallet addresses, read on-chain balances, apply market prices, and calculate a total. That is valuable, but incomplete. The same dollar balance can represent very different economic positions. A liquid stablecoin, a governance token in a thin market, collateral deposited into a lending protocol, and a claim on a liquidity pool may all appear beside one another while carrying different exit, smart-contract, and price risks.
A more useful mental model separates at least four dimensions. First is market exposure: how much value depends on the price of an asset, a correlated group of assets, or a volatile collateral ratio. Second is liquidity exposure: how quickly the position can be reduced without materially moving the market. Third is protocol exposure: the possibility that code, an oracle, an administrator, or a bridge fails. Fourth is operational exposure: incorrect approvals, compromised keys, phishing, wrong-chain transactions, and misunderstood contract behavior.
This distinction produces a non-obvious conclusion: diversification by token count is not necessarily diversification by risk. Ten assets may all depend on the same blockchain, stablecoin mechanism, bridge, or liquidity venue. Conversely, two positions may have different token names but share a common liquidation trigger. Tracking should therefore record relationships, not only balances. A lending position, for example, should be viewed alongside its collateral asset, borrowed asset, liquidation threshold, oracle dependency, and available exit liquidity.
Three approaches to DeFi portfolio oversight
Approach one: the spreadsheet or manual ledger
A spreadsheet remains useful for users who want explicit assumptions. It can distinguish principal from rewards, record realized and unrealized gains, and show whether a position is strategic, speculative, or reserved for taxes. For US users, this separation can also make the difference between a useful transaction history and a confusing pile of wallet activity when preparing records for tax reporting. Manual tracking is transparent: you know where the numbers came from.
Its weakness is timeliness and interpretation. On-chain positions change continuously, token prices move, and a manually entered balance can become stale at exactly the moment risk increases. A spreadsheet also struggles with complex positions such as liquidity-provider shares, rebasing assets, vesting claims, or collateral that can be liquidated automatically. It is best used as a long-horizon record and decision journal, not as the sole control layer for time-sensitive transactions.
Approach two: an automated portfolio dashboard
Automated trackers reduce the cost of observation. They can aggregate addresses and networks, estimate market values, identify token balances, and reveal concentrations that are easy to miss when each chain is viewed separately. This is particularly useful for an active DeFi user whose apparent diversification is spread across Ethereum, layer-two networks, and other compatible chains.
Automation, however, does not remove the need for judgment. A dashboard may rely on price feeds that are delayed, unavailable, or misleading for illiquid assets. It may classify a receipt token incorrectly, omit a debt position, or show a nominal value for an asset that cannot be sold at that price in realistic size. Cross-chain data can also create a false sense of one unified portfolio when settlement, bridge, and counterparty risks remain separate.
The practical rule is to treat automated valuation as an estimate, not a liquidation guarantee. Ask what price source is being used, whether debt and accrued obligations are included, and how the system handles assets with limited liquidity. The more complex the position, the more important it becomes to inspect the underlying protocol rather than relying on a summarized label.
Approach three: wallet-native review and transaction simulation
A security-focused wallet addresses a different part of the problem: the decision immediately before authorization. Transaction simulation attempts to show the expected state change before the transaction is broadcast. Instead of asking only, “What fee am I paying?” the user can ask, “Which assets will leave my wallet, which approvals will change, and what will I receive if the transaction behaves as represented?” When the simulation is understandable, it can expose an unintended token transfer or an approval broader than the user intended.
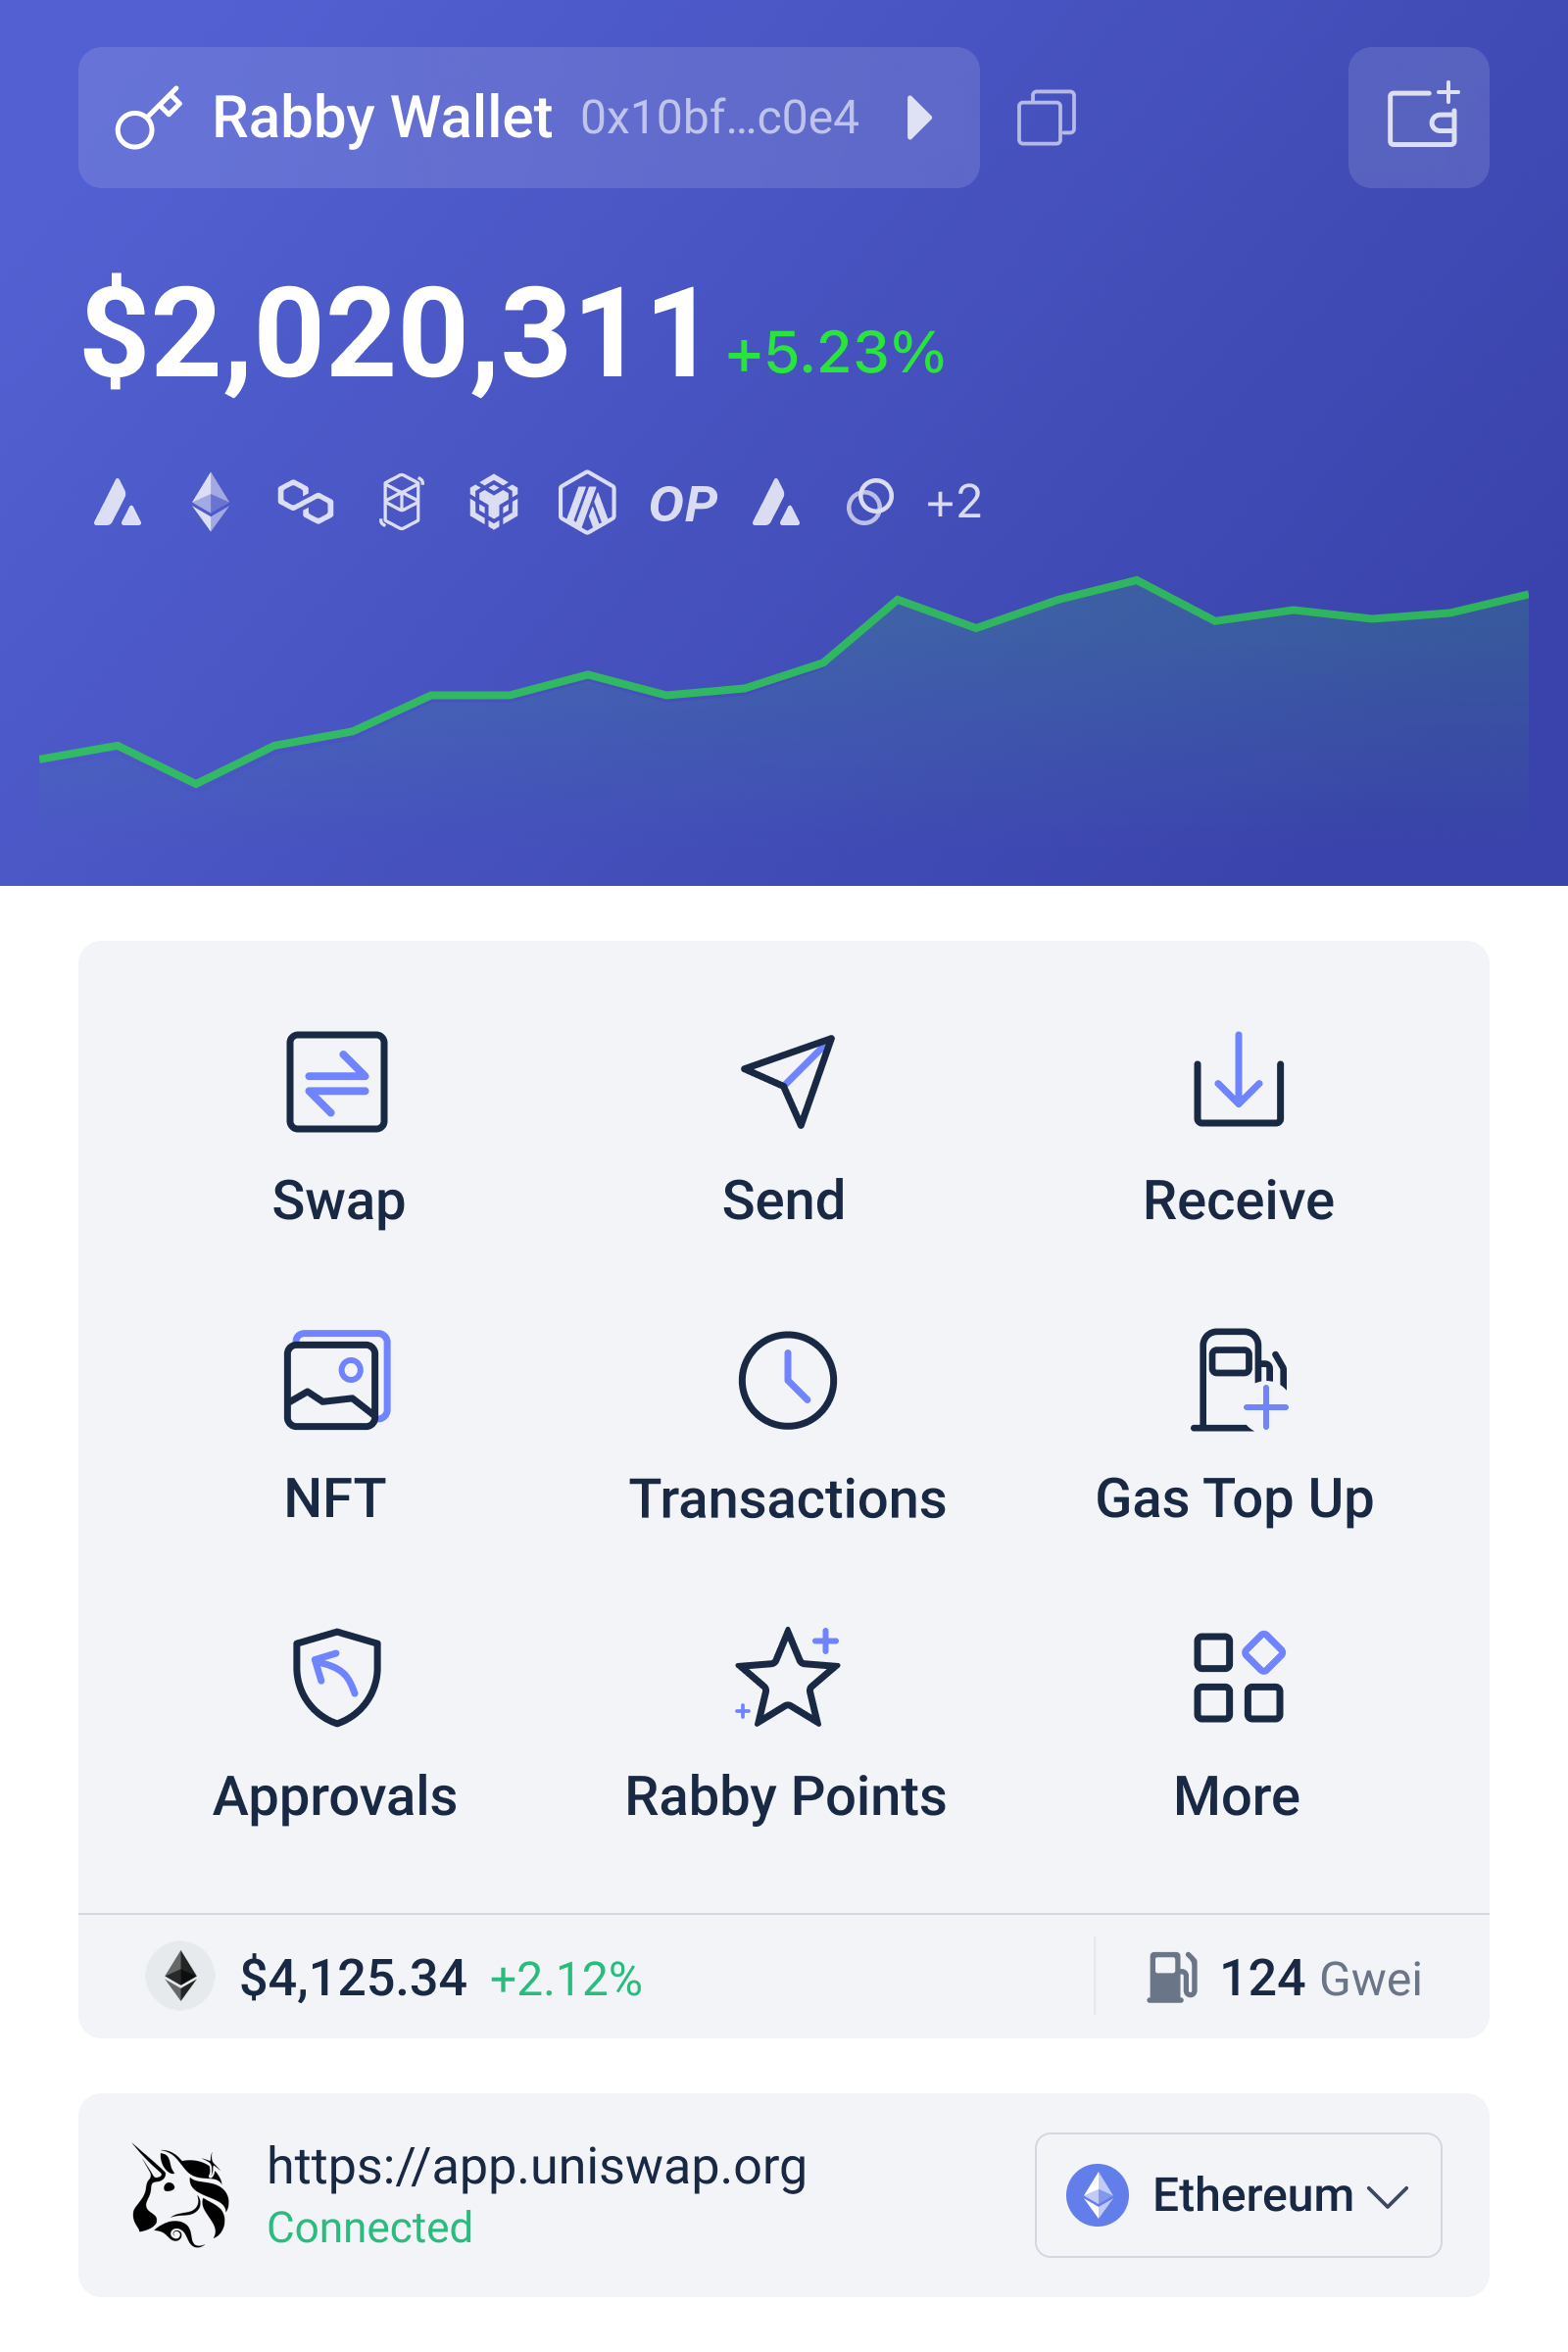
This approach is especially valuable against a common misconception: a transaction can be technically valid and still be economically dangerous. A malicious or compromised website may generate a transaction that the blockchain accepts while the user misunderstands its effects. Simulation cannot prove that a contract is safe, nor can it guarantee that the final on-chain state will match an estimate under all market conditions. It is a pre-execution control, not an audit and not a substitute for careful contract and permission review. Users seeking this type of workflow may find a rabby wallet useful to evaluate alongside their existing tracking tools, particularly when transaction interpretation is as important as balance display.
Where MEV protection fits
Maximal extractable value refers to value obtained by controlling or influencing transaction ordering, usually by observing pending transactions and arranging transactions around them. The most recognizable example is a large swap that reveals its intended trade to the public transaction queue. Other transactions may be placed before and after it, worsening execution for the original trader or capturing price movement created by the trade. Not every unfavorable fill is MEV: ordinary volatility, shallow liquidity, routing choices, and fees can produce similar outcomes.
MEV protection works by changing the information and ordering environment. A transaction may be sent through a private submission path, routed through an execution design that reduces exposure, or protected with limits such as slippage tolerance. Each method involves trade-offs. Private routing can reduce public visibility, but the user must trust the intermediary or relay and accept that availability may differ by network. Tight slippage limits can reduce losses from price movement and sandwiching, but they also increase the chance that a transaction fails. A larger tolerance improves execution probability while giving adverse price movement more room.
That trade-off shows why “MEV protection” is not a binary property. Protection depends on the transaction type, chain, route, liquidity, timing, and submission method. A small swap in a deep market has a different exposure from a large swap in a thin pool. A limit order, an aggregator route, and a direct automated-market-maker trade create different information footprints. The strongest workflow combines simulation, sensible slippage settings, review of the recipient and spender, and an execution path suited to the transaction.
A reusable decision framework
Before signing, separate three questions that are often collapsed into one screen. The first is portfolio question: what does this transaction do to my overall exposure? The second is contract question: what exact state change am I authorizing? The third is market-structure question: who can observe, reorder, or react to this transaction before it settles?
For portfolio exposure, identify whether the transaction increases leverage, concentration, bridge dependence, or reliance on a single protocol. For contract exposure, inspect approvals, recipients, permissions, and the difference between a one-time spend and an effectively unlimited allowance. For market-structure exposure, consider trade size relative to liquidity, slippage tolerance, whether the transaction is publicly visible, and whether failure would be preferable to execution at a worse price.
A simple risk register can make this operational. Label each position by market, liquidity, protocol, and operational risk, then mark whether the exposure is direct or shared with another position. Review the highest-impact risks first. A wallet holding a modest balance but carrying a large approval to an unfamiliar contract may deserve more immediate attention than a larger balance held without active permissions. This is a sharper use of attention than checking total portfolio value alone.
Limits, uncertainty, and what to watch next
No interface can eliminate smart-contract risk, oracle failure, validator behavior, private-relay dependence, or user error. Simulation is conditional on the state observed when it runs; markets can move between simulation, submission, and settlement. Portfolio values are conditional on available liquidity. MEV defenses can reduce one attack surface while introducing a different trust or availability assumption. These are boundary conditions, not reasons to abandon the tools. They are reasons to understand what each control actually guarantees.
The near-term direction of DeFi security is likely to be more integrated decision support, provided the underlying data and execution assumptions remain visible. A useful system would connect portfolio concentration with transaction simulation and execution risk: for example, warning not only that a swap may fail, but that it would leave a user excessively dependent on one volatile asset or reduce collateral safety. Whether such systems become genuinely reliable will depend on better treatment of complex positions, cross-chain context, and uncertainty rather than on more attractive dashboards.
Frequently asked questions
Is portfolio tracking enough to protect a DeFi user?
No. Tracking helps explain balances and exposures, but it does not necessarily inspect contract permissions, simulate state changes, or protect pending transactions from adverse ordering. It should be combined with transaction review and appropriate execution controls.
Does transaction simulation guarantee that a transaction is safe?
No. Simulation estimates what a transaction may do under a particular blockchain state. It can reveal unexpected transfers, approvals, or failures, but it cannot establish that the contract is trustworthy or that market conditions will remain unchanged before settlement.
How should a user choose between private routing and strict slippage limits?
They address related but different risks. Private routing can reduce public visibility, while strict slippage limits constrain the price damage the user will accept. The right choice depends on network support, route liquidity, transaction size, and whether a failed transaction is preferable to uncertain execution.
The central lesson is straightforward but easy to overlook: a DeFi portfolio is not merely a collection of balances. It is a set of changing claims, permissions, dependencies, and market interactions. Tracking explains what is held, simulation clarifies what a signature may change, and MEV-aware execution addresses how the transaction enters a competitive market. Used together—and interpreted with their limits in view—they turn a wallet from a passive display into a more disciplined risk-control process.
Deixe uma resposta
Want to join the discussion?Feel free to contribute!