Dust Attacks and Wallet Privacy: How Tangem’s Non-Custodial Design Protects Your Identity

A cryptocurrency holder receives a small deposit—sometimes a fraction of a cent—to a wallet address they use regularly. The amount is negligible, but the purpose is reconnaissance. A chain analyst, competitor, or surveillance operation has sent what is called a “dust attack,” a test to see if the recipient will move the funds and expose transaction patterns, address clustering, and spending behavior. The victim may consolidate dust into a larger transaction, accidentally linking multiple holdings and revealing activity across time and wallet implementations. This attack works because most users treat their wallet as a simple interface rather than understanding the relationship between custody, privacy, and transaction visibility.

Non-custodial hardware wallets present a fundamentally different privacy model than centralized exchanges or custodial platforms. When a service holds private keys on behalf of users, it sees every transaction, knows every address, and maintains internal records that can be requested, subpoenaed, or compromised. A non-custodial wallet like Tangem inverts that relationship: the user controls the private keys entirely, while the service never sees the secrets, addresses, or transaction history. That separation is the foundation of privacy. But a wallet that stores keys securely does not automatically prevent a user from exposing themselves through careless address reuse, obvious consolidation patterns, or connection to services that already know their identity. Understanding how Tangem’s design prevents certain attack surfaces while requiring active privacy discipline from users is essential for anyone trying to maintain actual ownership of cryptocurrency.

A Tangem card and ring hardware wallet showing NFC-based interaction with a mobile application for secure offline private key storage

The dust attack as a privacy diagnostic

A dust attack exploits a behavioral reality: most people do not want to leave small amounts in wallets unused. When they receive unexpected deposits, they eventually move them or consolidate them with other funds. This consolidation is traceable. If a user has received dust at address A, and address B in the same wallet receives a legitimate payment, an observer can watch for a transaction that spends outputs from both addresses in a single consolidation event. That transaction reveals that A and B are controlled by the same entity. Repeat this process across dozens of dust deposits and thousands of transactions, and a clear map of holdings and behavior emerges.

The attack is particularly effective against users who rely on custodial services or exchange wallets. If a user maintains a wallet on an exchange platform and receives dust, the exchange can see the incoming transaction immediately, note the address, track any consolidation attempt, and maintain records linking the deposit to the user’s account and identity. The exchange’s internal database becomes a chain-of-custody record for every movement the user makes. A regulatory request or accidental breach can then expose years of transaction history in one event.

A non-custodial wallet changes this dynamic because the service provider never sees the addresses or transactions. When using a non-custodial wallet like Tangem, dust arrives at an address that only the cardholder knows and controls. The wallet provider cannot log it, cannot alert the user to consolidation risk, and cannot be compelled to produce transaction records because none were created in their systems. This does not make dust disappear from the blockchain—the transaction is still public—but it breaks one critical chain: the connection between the user’s identity and the cryptocurrency addresses they control.

However, the user must still choose how to respond when they discover dust. If they immediately consolidate it with other outputs in a transparent way, the blockchain analysis remains possible. If they spend it carelessly to a service that identifies them (an exchange, a tracked merchant, or a payment processor), they have reconnected the link themselves. The wallet’s non-custodial design prevents the service provider from being the weak point; it cannot prevent the user from becoming one through their own choices.

Why key custody determines the privacy boundary

The most fundamental privacy distinction in cryptocurrency is who holds the private keys. If a service holds the keys, it has cryptographic proof that it can generate and sign transactions, meaning it has complete access to the funds and can observe or intercept every movement. It must also defend those keys against internal threats (rogue employees), external attackers (hackers targeting the service), and legal demands. If the user holds the keys, the service has no such access, no such liability, and no such records to produce. That asymmetry defines everything about privacy and security that follows.

Tangem wallet architecture implements this boundary through a secure element—a specialized cryptographic chip that generates private keys offline and stores them in encrypted, tamper-resistant memory. The card or ring never exposes the key material even to the mobile phone it connects to. When a transaction must be signed, the user brings the card near their phone using NFC, and the secure element performs the cryptographic operation internally, returning only the signature. The phone sees the transaction data and the signature, but never the private key. This is categorically different from a wallet application that stores keys in a phone’s memory, even if encrypted, because the key generation and signing operations occur in hardware that the user controls, not in software that their phone’s operating system or any application could potentially intercept.

This design immediately eliminates several attack surfaces. A compromised phone cannot extract the key. Malware cannot sign unauthorized transactions because the secure element requires physical proximity for signing. A backup of the phone’s data will not reveal the key. A thief who steals the phone cannot drain the wallet without the card. The user’s cryptocurrency remains secure even if they lose physical custody of the device they normally use to check balances and create transactions.

The custodial comparison is stark. An exchange, even one with security certifications, maintains private keys in its infrastructure. That infrastructure may use hardware security modules, cold storage, and access controls, but it is still centralized in one organization’s hands. A user who deposits funds to an exchange has transferred key custody to that organization. They can then access those funds only with permission—a password, two-factor authentication, and agreement to the exchange’s terms of service. If the exchange is hacked, goes bankrupt, or refuses withdrawal requests, the user has no cryptographic recourse. The funds are simply gone or inaccessible.

Address reuse and privacy costs in transparent blockchains

Bitcoin, Ethereum, and most major cryptocurrency networks record all transactions publicly and permanently. This means address reuse—using the same public address to receive multiple payments over time—creates a persistent, observable link between those payments. If Alice has received ten separate payments to address X, and then spends them together, it is mathematically clear that the same entity controlled all ten payments. An observer analyzing the blockchain can cluster related addresses and infer holdings, spending patterns, and even personal identity if the user has ever connected an address to a known service or person.

Tangem addresses this through deterministic key derivation, allowing users to generate a nearly unlimited number of distinct addresses from a single card. Each address can be used for a single receiving context or person, preventing consolidation patterns from being obvious. When a user later needs to spend, they can choose which addresses to consolidate based on privacy and efficiency trade-offs rather than being forced to use whatever address had the lowest balance. This capability exists in many wallets, but it matters more when the wallet is non-custodial because the user has no intermediary filtering or analyzing the choice. The service provider cannot intercede, cannot log preferences, and cannot create correlations.

However, this strength also reveals a user discipline requirement. Generating diverse addresses is meaningless if the user then spends them carelessly. For example, if Alice uses address X1 to receive payment from her employer, and address X2 to receive payment from a friend, and then spends both X1 and X2 together, the blockchain still shows consolidation. An observer cannot see that one payment was employment income and the other was personal, but they can see that the same entity controlled both. More importantly, if the employer or friend has any visibility into the blockchain (many services now provide this), they can observe that the payment they sent was later combined with other funds, potentially revealing Alice’s spending patterns to people who otherwise would not know them.

The real privacy lesson is that address reuse and consolidation are visible whether or not the wallet is custodial. The custodial difference is that a centralized service would know the connection anyway. A non-custodial design simply refuses to be a weak point. If the user then re-creates the link through their own behavior, that is a different problem—one that requires education and discipline, not a better wallet.

Seedless backups and the recovery phrase trade-off

Traditional hardware wallets ask users to write down a recovery phrase—typically 12 or 24 words—when they first set up the device. This phrase is the master secret from which all private keys are derived. If the hardware wallet is lost or damaged, the recovery phrase can be imported into another wallet to restore all funds. The assumption is that users will store this phrase in a physically secure location, never photograph it, and never enter it into any computer. In practice, many users violate these rules.

Tangem eliminates the recovery phrase entirely by offering what is called a “seedless” backup system. Instead of writing down words, users can create one or more additional backup cards. If the primary card is lost, the backup card can restore the wallet. The backup card is itself a secure element with the same tamper resistance and isolation as the primary card. This removes the most dangerous vulnerability: a text file, notebook, or photographed phrase that a thief, family member, or housekeeper could discover.

The backup card approach introduces a different risk: managing multiple physical objects. A user with two cards must decide which to use daily, where to store the backup, and how to verify that it actually works if a recovery becomes necessary. Some users may find multiple cards more secure than a written phrase; others will find them more burdensome. The trade-off is worth understanding explicitly. A recovery phrase written carefully and stored securely might be extremely safe; a backup card stored carelessly in a desk drawer is not. Conversely, a recovery phrase that someone enters into a cloud backup application or a text editor is catastrophically vulnerable, while multiple backup cards reduce that particular vector.

The option to create backup cards also affects privacy in one subtle way. If a user creates a backup card and stores it with someone else (a family member, a safe deposit box at a bank, or a escrow service), that party has access to the wallet’s recovery mechanism. They cannot see individual transactions or addresses unless the user reveals them, but they can potentially restore the wallet and access all funds if the primary card is lost and the user is unavailable. This is a trust and custody relationship, different from the primary card’s isolation but worth considering in security planning.

NFC-based signing and the absence of browser extension risk

Most cryptocurrency users interact with decentralized applications through a browser extension wallet like MetaMask or Phantom. The extension has constant access to the browser, can see the websites the user visits, and can intercept transactions before they are signed. A malicious website can trick the extension into signing transactions, sometimes simply by requesting a signature for what appears to be an innocuous message. A compromised or malicious extension can drain wallets by signing unauthorized transactions or by stealing private keys if the extension stores them directly.

Tangem removes the browser extension from the signing chain entirely. A decentralized application connects to the wallet through a standard protocol (WalletConnect or similar) that sends transaction data to the mobile application, never to a browser extension. The user views the transaction details in the Tangem app, confirms them by bringing the card near the phone, and the secure element signs the transaction. The browser never sees the private key, never participates in the signing process, and cannot intercept or redirect funds. This is a substantial reduction in attack surface.

The trade-off is speed and convenience. Signing through an extension is nearly instantaneous once the request appears. Signing with a hardware card requires the user to have the card physically present and to perform an NFC interaction, which takes a few seconds and requires awareness of what is being signed. For frequent transactions, this is slower. For high-value or infrequent transactions, the friction is actually beneficial because it encourages the user to read the transaction details before approving.

The NFC-based confirmation model also reveals another privacy dimension. Unlike a browser extension that might sign in the background or respond to automated requests, the Tangem card requires user presence and intention. This does not prevent a user from being tricked into signing a harmful transaction by a deceptive interface, but it does require intentional action rather than passive background processing. A scammer cannot drain the wallet through a vulnerability in the extension layer or through silent authorization requests.

Decentralized node selection and transaction broadcasting privacy

When a transaction is signed and ready to broadcast, the question becomes: which network node receives it, and can that node or others observe identifying information about the sender? If a user’s wallet directly connects to their own node, and that node is running on their own infrastructure or through a trusted privacy-focused service provider, then the broadcast is routable through layers that do not see the IP address or do not correlate transactions with user identity. If the wallet uses a public node provider, the provider’s servers see the IP address, the transaction data, and can correlate multiple transactions if they come from the same IP over time.

Tangem’s non-custodial design does not inherently solve this problem because it is a network-layer issue, not a key-custody issue. Whether the wallet is custodial or non-custodial, the transaction still goes somewhere to be broadcast. What the design does is ensure that the wallet provider itself is not the intermediary. Users can configure which node providers the wallet connects to, can choose to route through Tor or a VPN, and can use their own node if they operate one. The wallet does not have a business interest in observing these details because it does not maintain a database of user transactions.

Compare this to a custodial exchange. The exchange receives the transaction from the user, broadcasts it from its own infrastructure, and maintains internal records of when the transaction was submitted, what the network fee was, and whether it succeeded. The exchange’s logs contain a detailed history of the user’s transaction activity. A regulatory request or breach of the exchange’s systems exposes this history all at once. A non-custodial wallet provider has no equivalent logs to produce because the transaction was created and broadcast entirely by the user’s device, not submitted to the provider’s systems.

Multi-chain support and privacy complexity across networks

Tangem supports thousands of cryptocurrencies across dozens of blockchains: Bitcoin, Ethereum, Litecoin, Polygon, Solana, and thousands of ERC-20 tokens among them. This convenience means a user can hold multiple assets without multiple wallets or recovery phrases. It also means a user might consolidate holdings across multiple networks without understanding the privacy implications of each network’s transaction model.

Bitcoin, for example, exposes transaction amounts, inputs, and outputs publicly. Privacy techniques like PayJoin or coin control can help, but the default transaction is transparent. Ethereum shows similar information: the sending address, receiving address, amount transferred, and all contract interactions are visible to everyone. Some tokens operate on privacy-focused networks like Monero, but most do not. A Tangem wallet that holds both Bitcoin and Ethereum can execute transactions on both networks, but a user cannot assume that the privacy properties are equivalent. Moving funds between networks or consolidating holdings across networks can create chain-analysis opportunities if an observer is watching both blockchains.

The wallet itself handles this correctly by keeping the keys isolated and the signing process secure. The problem belongs to the user: understanding which assets have which privacy properties, which consolidation patterns are observable, and whether any of the addresses or transactions can be linked to known identity information. A secure crypto storage solution prevents the service provider from being the weak point, but it does not prevent the user from being careless. Tangem’s role is to ensure the keys are protected and the wallet provider has no visibility into transactions. The rest is user behavior.

The practical privacy hierarchy: what actually matters

When evaluating wallet privacy, users should think in layers. The first layer is key custody: who holds the private keys. A non-custodial design like Tangem’s is substantially better than custodial alternatives because the service provider cannot see transactions, maintain records, or be a target for regulatory demands. This is foundational and worth the effort to maintain. The second layer is key security: can the keys be extracted or used without authorization. Hardware-based signing with offline key generation addresses this. The third layer is address and transaction management: does the wallet encourage diverse addresses, careful consolidation, and appropriate privacy techniques for each network. The fourth layer is network privacy: can an observer identify the IP address, the timing of transactions, or the connection to wallets. The fifth layer is user behavior: does the user understand these issues and avoid obvious mistakes like reusing addresses across identified and unidentified contexts.

Tangem excels at the first two layers. It provides excellent tools for the third layer through address derivation and deterministic key generation. It leaves the fourth and fifth layers to the user. This is appropriate because network privacy and behavioral discipline are not problems that a wallet can solve unilaterally. A user can undo all of a wallet’s privacy benefits by consolidating dust carelessly or by moving funds to a service that already knows their identity. The wallet’s contribution is to ensure that it never becomes a choke point where third parties are forced into visibility.

For anyone concerned about cryptocurrency privacy and ownership, the distinction between custodial and non-custodial is the first and most important decision. All the privacy techniques, secure signing processes, and address management tools follow from that choice. Tangem makes that choice concrete by implementing a non-custodial design with offline key generation, hardware-based security, and no service-side access to private keys or transaction history. You can explore a secure hardware wallet for crypto storage to understand the practical implementation, but the underlying principle is simple: if the wallet provider cannot see the transaction, they cannot be forced to reveal it, and they cannot inadvertently leak it through poor security or negligent practices.

Frequently asked questions

Can dust attacks harm my cryptocurrency if I use Tangem?

Dust attacks cannot drain funds because Tangem is non-custodial—only you can sign transactions. However, the dust amount will still appear on the blockchain. The real risk is that you consolidate the dust with other funds in an obvious way, linking addresses that should have remained separate. Tangem helps by allowing you to generate diverse addresses and control consolidation carefully, but the blockchain visibility remains unchanged.

Why does Tangem not use a recovery phrase like other hardware wallets?

The seedless backup system uses additional hardware cards instead of written words. This eliminates the risk that someone will photograph, digitize, or discover your recovery phrase. However, you then need to manage and protect multiple physical cards. Both approaches have trade-offs; neither is universally superior in every situation.

How does Tangem protect my privacy from the wallet provider?

Tangem never sees your private keys, addresses, or transactions because signing happens entirely on the secure element chip in the card. No transaction records are created by the provider. This is fundamentally different from custodial wallets where the service maintains complete records of your activity. However, your privacy still depends on which nodes you broadcast to and whether you reuse addresses in ways that link your transactions together.
Descargar Cake Wallet: cómo funciona una billetera de privacidad para Monero y otros activos

Imaginemos una situación frecuente: una persona en España, Estados Unidos o Latinoamérica recibe Monero y quiere guardarlo en el móvil sin depender de una plataforma de intercambio. Busca “descargar Cake Wallet”, instala una aplicación y espera que el problema termine ahí. Sin embargo, una billetera no es simplemente una cuenta con una interfaz cómoda. Es un sistema que administra claves, construye transacciones y comunica información con una red. Entender esa cadena importa más que reconocer un logotipo: una decisión correcta durante la instalación puede proteger los fondos, mientras que una copia de seguridad mal entendida puede volverlos irrecuperables.

Cake Wallet resulta especialmente interesante como caso de estudio porque se asocia con el uso de Monero y también con otros activos digitales. Su propuesta se apoya en la autocustodia: las claves están bajo control del usuario, no de un intermediario que pueda congelar una cuenta o restablecer el acceso por correo electrónico. Esa ventaja tiene un reverso inevitable. Si el usuario pierde la frase de recuperación o la expone, la responsabilidad no se transfiere a un servicio de atención al cliente. La privacidad, en este contexto, no es una función aislada; es una combinación de criptografía, hábitos operativos y control del dispositivo.

Identidad visual de Cake Wallet como punto de partida para analizar autocustodia y privacidad en Monero

Qué ocurre realmente al usar una aplicación de este tipo

Una billetera de criptomonedas no almacena monedas como si fueran archivos dentro del teléfono. En redes como Monero, los fondos se registran en la cadena de bloques y la aplicación conserva las claves necesarias para demostrar que el usuario puede gastar determinadas salidas. La clave privada firma la transacción; la red verifica esa firma sin revelar el secreto. Por eso una aplicación puede mostrar un saldo, preparar un pago y transmitirlo, pero no “recuperar” mágicamente una cuenta si se pierde la información criptográfica de respaldo.

El primer paso al instalar Cake Wallet debería ser distinguir entre tres elementos: la aplicación, la red y el respaldo. La aplicación es la herramienta de interacción. La red valida y registra las operaciones. El respaldo —normalmente una frase o conjunto de datos de recuperación— permite reconstruir el acceso en otro dispositivo compatible. Confundir estos niveles produce errores comunes: creer que borrar la aplicación borra los fondos, pensar que una contraseña local sustituye a la frase de recuperación o asumir que una captura de pantalla es un método seguro de custodia.

Para quien busque información de descarga, la prudencia empieza antes de pulsar “instalar”. Es recomendable descargar cake wallet únicamente después de comprobar el dominio, la procedencia del archivo y la compatibilidad con el sistema operativo. Las aplicaciones falsas pueden imitar nombres, colores y descripciones, pero capturan frases de recuperación en lugar de protegerlas. Una práctica útil es comparar la información publicada en los canales oficiales del proyecto, revisar los permisos solicitados y evitar enlaces reenviados por mensajes privados o anuncios que prometen recompensas.

Privacidad: más que ocultar un saldo

Monero utiliza mecanismos de privacidad que dificultan vincular públicamente una transacción con un remitente, un receptor y una cantidad de la manera habitual en muchas cadenas transparentes. La billetera participa en ese proceso mediante la selección de salidas, la generación de datos de pago y la firma de la operación. La idea importante es que la privacidad no depende solo de una pantalla que diga “privado”; depende de cómo se construye y se comunica cada transacción.

Hay, no obstante, una distinción decisiva entre privacidad en la cadena y privacidad en el dispositivo. La primera se refiere a la información que terceros pueden inferir observando la red. La segunda incluye el teléfono, las copias de seguridad, las notificaciones, el historial de portapapeles, las capturas de pantalla y la conexión utilizada. Un teléfono desbloqueado, una frase almacenada en una nube insegura o una dirección pegada en una aplicación maliciosa pueden revelar información aunque el protocolo tenga fuertes propiedades de privacidad.

También conviene comprender el papel de los nodos. Para consultar saldos y transmitir operaciones, una billetera necesita comunicarse con infraestructura de red. Según la configuración, puede utilizar un nodo remoto o uno controlado por el propio usuario. El nodo remoto facilita la experiencia, especialmente para principiantes, pero introduce una relación de confianza operacional: ese servidor puede observar ciertos metadatos de conexión o disponibilidad, aunque no obtenga automáticamente las claves privadas. Ejecutar infraestructura propia ofrece más control, pero requiere conocimientos, mantenimiento y una conexión estable. No existe una opción universalmente superior; existe un intercambio entre comodidad, independencia y exposición de metadatos.

El caso práctico: recibir, guardar y gastar

Supongamos que una usuaria recibe Monero por primera vez. Antes de aceptar un pago importante, debería crear la billetera en un dispositivo actualizado, anotar el respaldo fuera de línea y confirmar que puede restaurarlo siguiendo un procedimiento controlado. Después puede recibir una cantidad pequeña y comprobar que el saldo aparece correctamente. Esta prueba no elimina todos los riesgos, pero reduce la probabilidad de descubrir un error de copia cuando ya hay una suma relevante en juego.

Al enviar fondos, la atención cambia. La usuaria debe verificar el destino, la cantidad, la comisión y el estado de la red. En contextos de privacidad, la rapidez visible en la pantalla no equivale necesariamente a confirmación económica final. Una transacción puede estar creada, transmitida y pendiente de confirmaciones. Además, los pagos irreversibles exigen confirmar cuidadosamente la dirección: una transferencia enviada a un destino incorrecto no suele poder deshacerse mediante una reclamación.

La compatibilidad con varios activos puede ser conveniente, pero también añade complejidad. Cada red tiene reglas, formatos de dirección, comisiones y modelos de confirmación diferentes. Una interfaz unificada puede hacer que todo parezca igual cuando no lo es. El criterio más seguro consiste en tratar cada activo como un sistema distinto: comprobar la red seleccionada, utilizar la dirección adecuada y realizar primero una operación pequeña. La sencillez visual no debe confundirse con equivalencia técnica.

Seguridad operativa y límites de la autocustodia

El respaldo es el centro de gravedad de la autocustodia. Debe escribirse de forma legible, conservarse en un lugar protegido frente a pérdida, humedad, robo y acceso no autorizado, y nunca compartirse con una persona que no deba controlar los fondos. Guardarlo en una fotografía, correo electrónico o documento sincronizado puede ser cómodo, pero amplía la superficie de ataque. Una contraseña de desbloqueo protege el acceso cotidiano al teléfono; la frase de recuperación protege la capacidad de reconstruir la billetera. Son capas distintas.

La autocustodia tampoco convierte al teléfono en una caja fuerte. Un dispositivo con sistema desactualizado, aplicaciones de origen dudoso o acceso físico sin protección puede comprometer claves. Para cantidades importantes, algunos usuarios prefieren separar el dinero destinado al uso diario del ahorro de largo plazo y emplear dispositivos o procedimientos más estrictos. Esa separación introduce una pequeña fricción, pero reduce el impacto de un incidente aislado.

Hay otra limitación menos visible: las propiedades de privacidad pueden verse afectadas por el comportamiento del usuario. Publicar en redes sociales que una dirección corresponde a una persona, reutilizar rutinas identificables o revelar voluntariamente datos de pago puede crear conexiones fuera de la cadena. La criptografía puede dificultar la observación automática, pero no corrige una identidad expuesta por contexto. La privacidad funciona mejor como disciplina integral que como botón de activación.

Qué debería observar un usuario antes de decidir

La pregunta adecuada no es solo “¿es Cake Wallet fácil de usar?”. Conviene preguntar qué necesita proteger el usuario, contra quién y con qué nivel de complejidad está dispuesto a convivir. Para pagos pequeños y frecuentes, una aplicación móvil puede ofrecer un equilibrio razonable entre acceso y control. Para ahorros relevantes, la decisión debería incorporar un plan de respaldo, separación de fondos, actualizaciones verificadas y un procedimiento de recuperación probado.

En el corto plazo, los indicadores más útiles no son las promesas publicitarias, sino la claridad de las instrucciones, la transparencia sobre las redes compatibles, la calidad de las actualizaciones y la facilidad para verificar el origen de la aplicación. No se dispone aquí de novedades recientes específicas del proyecto que justifiquen una predicción sobre su evolución. Por eso, el enfoque más sólido es condicional: si una billetera mejora la verificación de transacciones y mantiene una experiencia comprensible sin ocultar sus límites, puede reducir errores de usuarios nuevos; si prioriza únicamente la simplicidad visual, podría aumentar la confusión entre activos y niveles de seguridad.

Para lectores hispanohablantes, también importa el contexto local. Las comisiones, los servicios de intercambio disponibles y las obligaciones fiscales pueden variar entre España, Estados Unidos y los países de Latinoamérica. Una billetera facilita el control técnico de los fondos, pero no sustituye el cumplimiento de las normas aplicables ni elimina la necesidad de registrar operaciones cuando la legislación lo exige. Privacidad financiera y ocultación de obligaciones legales son conceptos diferentes.

Preguntas frecuentes sobre Cake Wallet

¿Cake Wallet guarda mis monedas dentro del teléfono?

No en el sentido convencional. Los fondos existen como registros en la red correspondiente, mientras la aplicación administra las claves y permite firmar operaciones. Por eso la frase de recuperación es fundamental: quien la controla puede reconstruir el acceso, y quien la pierde puede perderlo de forma permanente.

¿Una billetera de privacidad garantiza anonimato total?

No. Puede incorporar mecanismos que reduzcan la información visible en la cadena, pero el dispositivo, los metadatos de conexión, los intercambios, las copias de seguridad y la conducta pública del usuario siguen siendo relevantes. La privacidad es una propiedad con límites y depende tanto del protocolo como de la operación cotidiana.

¿Es mejor utilizar un nodo remoto o uno propio?

Depende del equilibrio buscado. Un nodo remoto suele simplificar la configuración, mientras que uno propio ofrece mayor control sobre la infraestructura y ciertos metadatos. El segundo exige conocimientos, mantenimiento y recursos; elegirlo no es automáticamente más seguro si se administra de forma deficiente.

Descargar una aplicación de billetera es el comienzo, no el resultado final. La decisión verdaderamente importante consiste en comprender qué controla la aplicación, qué depende de la red y qué responsabilidad permanece en manos del usuario. Cake Wallet puede servir como una puerta accesible hacia Monero y otros activos, pero su valor práctico aparece cuando la comodidad se acompaña de verificación, respaldo y una visión realista de los límites de la privacidad.

Ledger Live App, Ledger Device, and Ledger Live Install: Choosing the Right Setup for Safer Crypto

A hardware wallet does not make cryptocurrency custody “safe” by itself. In practice, the most important security boundary is the interaction between three separate components: the Ledger device that protects private keys, the Ledger Live app that organizes accounts and transactions, and the computer or phone used to access the software. That may sound less reassuring than a one-product promise, but it is a more useful mental model. Security comes from how these parts divide responsibility—and from whether the user recognizes when they are being asked to cross a dangerous boundary.

For US crypto users, the choice between Ledger Live desktop and mobile is therefore not simply a matter of screen size. Desktop is often more comfortable for account management, portfolio review, and careful transaction inspection. Mobile is more convenient for quick checks and on-the-go approvals. Neither replaces the hardware wallet, and neither eliminates phishing, malicious approvals, address substitution, network mistakes, or the consequences of losing a recovery phrase. The right setup depends on the task, the user’s habits, and the amount of operational risk involved.

How the three-part system actually works

A Ledger device is designed to keep private keys isolated from the general-purpose operating system. A private key is the secret that authorizes blockchain transactions; it is not supposed to be copied into a website, email, cloud account, or ordinary app. The device signs a transaction internally, while the connected Ledger Live software helps display balances, prepare transactions, and communicate with supported networks. The signing step is the critical distinction: the computer or phone can request an action, but the device is intended to approve it only after the user reviews it.

Ledger Live functions as a management layer rather than a vault in the same sense as the device. It may show accounts, transaction history, portfolio information, and network-specific options, but visible information on a screen should not automatically be treated as proof that an action is legitimate. A compromised computer could display misleading information. That is why the device screen remains an important checkpoint, particularly when confirming a recipient address, amount, network, or smart-contract interaction.

This produces a useful distinction between key security and decision security. The hardware wallet primarily strengthens protection of the keys. It does not guarantee that a user will send funds to the right address or approve a harmless contract. Many losses in crypto occur not because a private key was directly extracted, but because a user authorized a transaction whose consequences were misunderstood. Hardware protects the authorization mechanism; human review still determines what gets authorized.

Ledger Live desktop versus mobile

Desktop: better for deliberate, complex work

Ledger Live desktop is generally the stronger choice when the task requires concentration. A larger display can make it easier to compare addresses, review transaction details, manage several accounts, and understand how a portfolio is distributed. Users who interact with decentralized applications, or dApps, may also find a computer more practical because browser-based workflows and wallet connections can become difficult to inspect on a small screen.

The trade-off is that a desktop computer usually has a larger attack surface than a dedicated signing device. It may contain browser extensions, messaging software, downloads, saved passwords, remote-access tools, or malware. The Ledger device is intended to limit the damage that this environment can cause, but it cannot turn an infected computer into a trustworthy display. A user who ignores warnings or approves an unfamiliar contract can still lose assets even when the private key never leaves the device.

Desktop is best understood as the “slow lane” for meaningful decisions: installing updates from a trusted source, adding accounts, checking network compatibility, preparing transfers, and reviewing unusual activity. Convenience matters, but deliberate friction can be protective when a transaction is irreversible.

Mobile: better for access, weaker for context

The Ledger Live mobile app is useful when portability matters. It can help users check balances, monitor activity, and manage supported accounts while away from a home computer. A phone may also be easier to keep physically close to the hardware wallet during a routine transaction. For users who value quick access, mobile can reduce the temptation to use an unfamiliar public computer.

Yet a phone’s smaller screen can make context harder to assess. Long addresses, token names, network identifiers, and contract details are difficult to compare at a glance. Mobile operating systems also contain their own risks, including malicious apps, screen overlays, account takeover, SIM-related attacks, and unsafe backups. These risks do not mean mobile is unsuitable; they mean the convenience advantage should not be confused with a security advantage in every situation.

A practical rule is simple: use mobile for observation and low-complexity actions, and prefer desktop—or a more controlled workflow—for larger transfers, new counterparties, unfamiliar networks, and decentralized finance activity. This is a heuristic, not a guarantee. A careful mobile user may be safer than a careless desktop user, because behavior often matters more than the category of device.

Installing Ledger Live without weakening the security model

The installation process is part of the security procedure, not a preliminary chore. Users should obtain the application through a source they can independently verify and be cautious of search advertisements, copied support pages, unsolicited messages, and download prompts that ask for a recovery phrase. A legitimate support workflow should never require a secret recovery phrase to “synchronize,” “validate,” or “unlock” a device. Anyone who requests that phrase is asking for the master credential to the wallet.

Readers comparing installation routes can begin with the ledger live download information, then verify that the application name, publisher details, and update behavior match the expected Ledger software before entering sensitive information or connecting accounts. The link itself should not be treated as a substitute for independent verification. The safer habit is to inspect the source, avoid unofficial copies, and never install urgent “security patches” delivered through random direct messages.

After installation, pair the Ledger device according to the on-screen instructions and confirm that the device is genuine through the application’s supported verification process. Keep the recovery phrase offline and private. It is a backup for restoring control, not a password for customer service and not something to photograph or store in a cloud drive. Anyone who obtains it may be able to reconstruct the wallet elsewhere, regardless of whether the original Ledger device remains in the owner’s possession.

Updates deserve a balanced view. New software can improve compatibility, fix defects, and support changing networks, but an update also creates an opportunity for impersonation or user error. The best practice is not “never update” or “update immediately from any prompt.” It is to update through a trusted channel, read what is being requested, and pause if the process asks for information that should remain secret.

DeFi and Web3: where the comparison becomes more complicated

Recent Ledger messaging has emphasized pairing the crypto wallet with the Ledger Wallet app to manage portfolios and access dApps and Web3 services. That direction reflects a real shift in the category. Hardware wallets were once used mainly for holding and sending a relatively small set of assets. Today, users may sign token approvals, interact with decentralized exchanges, mint digital assets, bridge between networks, or participate in other smart-contract systems.

The benefit is broader utility without exposing the private key to a website. The limitation is that a hardware wallet cannot make a smart contract honest. A user can approve a contract that has excessive spending permissions, sign a transaction on the wrong network, or misunderstand a complex payload. In these situations, the device is functioning as designed: it is protecting the key while honoring the user’s approval.

This is the non-obvious trade-off of self-custody. More control can mean more responsibility at the point of authorization. Users should separate long-term holdings from experimental activity where practical, review token approvals, use small test transactions for unfamiliar workflows, and avoid treating a familiar interface as evidence that every connected dApp is safe. The Ledger Live app can improve visibility, but visibility is not the same as interpretation.

A decision framework for US users

Choose desktop when the transaction is large, unusual, technically complex, or difficult to verify on a phone. Choose mobile when the main need is monitoring, routine management, or access while traveling. Use the Ledger device for final approval in either case, and treat the device screen as an independent checkpoint rather than a formality.

It is also worth planning for failure. What happens if the phone is lost? What if the laptop is infected? What if the device stops working? The recovery phrase is the continuity mechanism, so its storage deserves more attention than the app interface. A secure backup location, protection from fire or water, and a clear inheritance or emergency plan may matter more over several years than small differences between desktop and mobile design.

Looking ahead, the key signal is not merely whether wallet software adds more Web3 features. It is whether interfaces make transaction intent easier to understand before signing. If dApps become more capable while transaction descriptions remain opaque, users may face a widening gap between technical control and informed consent. If wallet software improves human-readable warnings, permission management, network clarity, and recovery education, the same hardware foundation could support safer participation. That outcome is conditional: it depends on interface design, user behavior, and the quality of the surrounding ecosystem.

Ledger Live and Ledger Device FAQ

Is Ledger Live the same thing as a Ledger hardware wallet?

No. Ledger Live is software used to manage accounts and communicate with supported blockchain networks. The Ledger device is the hardware component intended to keep private keys isolated and sign transactions. They work together, but they serve different security roles.

Should I use Ledger Live desktop or the mobile app?

Use desktop when you need more context for complex transactions, multiple accounts, or dApp workflows. Use mobile for convenient monitoring and simpler routine actions. In both cases, verify the important details on the Ledger device before confirming.

Can Ledger Live protect me from every crypto scam?

No. It can support safer key management, but it cannot guarantee that a website, token, smart contract, or recipient is legitimate. Never share the recovery phrase, be skeptical of urgent support requests, and treat unfamiliar approvals as high-risk actions.

What is the most important installation mistake to avoid?

Do not install software from an unverified copy or enter the recovery phrase into an app, website, form, or support chat. Installation should preserve the wallet’s security boundary, not create a new path for someone else to obtain the credentials that control it.

When a Single Seed Phrase is Not Enough: Practical Security with a Ledger Nano

Picture this: you’re at a coffee shop in Brooklyn, you’ve just moved a significant portion of your savings into crypto, and your phone buzzes — someone has reset an exchange account and started a withdrawal. Panic is the natural first response, but the real question is: how would a hardware wallet like a Ledger Nano change what’s possible in that moment? For many U.S. users the difference is not mystical — it’s procedural. A hardware wallet changes which actions are needed to move funds, who must be contacted, and how attack surfaces line up.

This article drills into how Ledger Nano hardware wallets work, why hardware custody meaningfully reduces specific risks, and where those protections stop. I explain the mechanisms that matter (secure elements, transaction signing, and air-gapped verification), compare trade-offs (usability vs. assurance, recovery complexity vs. single-point risk), and finish with decision-useful heuristics: when to use a hardware wallet, how to layer protections, and which signals to watch next in the evolving Web3 landscape.

Mechanics First: How a Ledger Nano Reduces Attack Surfaces

At a mechanical level a Ledger Nano is a small, tamper-resistant device that holds private keys inside a secure chip and signs transactions when you explicitly approve them on-device. Two mechanisms are central.

First, private keys never leave the device. Software on your phone or computer constructs an unsigned transaction, sends it to the device, and the device signs it inside its secure element. That signed transaction returns to the host and is broadcast. The critical implication: malware on your laptop can see unsigned transactions and try to trick you, but it cannot extract the private key or sign transactions without the device’s explicit approval.

Second, the device enforces explicit local verification. Good hardware wallets require you to confirm key transaction details (recipient address, amount) on the device screen itself. That local verification reduces remote tampering risk: an attacker who has compromised your PC can still attempt a “clipboard swap” or present a manipulated interface, but they cannot change what appears on the Ledger’s small display unless they also compromise the device itself.

These mechanisms are not unique to a Ledger Nano but are implemented in practice with varying degrees of engineering maturity and user experience. Today’s Ledger devices combine a secure chip designed to resist extraction, a separate microcontroller for the firmware, and a workflow that pushes verification onto the physical device. The most recent product updates also integrate with apps and dApps so users can manage DeFi access without exposing seed material — an increasingly important capability as DeFi and Web3 interactions become common.

Where Hardware Custody Really Helps — and Where It Doesn’t

Hardware custody shifts the locus of trust from online services and general-purpose devices to a small, purpose-built device. That pays off against a few common threat models:

– Remote compromise of an exchange or custodial service: If your private keys are in a hardware wallet, a hacking event at an exchange won’t automatically empty your balance. You avoid counterparty risk because custody resides with you.

– Malware on your everyday computer or phone: Keyloggers, clipboard hijackers, and phishers become less effective because they can’t sign transactions without the device and your physical confirmation.

– Social engineering attempts to get you to reveal mnemonic phrases: A Ledger Nano makes it clearer that revealing a seed phrase is the single action that hands total control to an attacker — and modern onboarding emphasizes never entering your seed into a computer or phone.

But it would be a mistake to treat hardware custody as a panacea. There are realistic limits and failure modes that matter in the U.S. context:

– Physical theft or coercion: If an adversary steals both your device and your written recovery phrase (or coerces you to reveal it), hardware custody no longer protects your funds. Operational security and secure storage of recovery material remain essential.

– Supply-chain attacks and tampering: While secure elements resist direct extraction, targeted supply-chain attacks that modify firmware or intercept devices before delivery are an adversarial concern. Mitigations include buying from reputable channels, checking device provenance, and following device initialization checks.

– Human error in recovery: Seed phrases are long and error-prone. Users who split phrases, use third-party backups, or DIY multisig without understanding the trade-offs can accidentally create single points of failure or reconstructability that weaken security.

Trade-offs: Usability, Recovery, and Advanced Custody

Security is always a trade-off. A useful mental model is to think in three dimensions: access control (who can sign), recovery resilience (what happens if you lose a device), and operational friction (how easy daily use is).

– Single-device model (typical Ledger Nano use): Low friction for daily use, high assurance against remote attack, but recovery depends fully on your seed phrase. If you lose both the device and your phrase, funds are irretrievable.

– Seed-splitting or custodial backups: Some users split their seed phrase across locations (safes, bank deposit boxes). This increases recovery resilience but introduces coordination complexity and potential for incomplete recovery if pieces are lost. It also raises the risk of multiple compromise points.

– Multisignature setups: Using multiple devices or co-signers increases resilience — an attacker needs to compromise several devices or people. The trade-off is higher operational complexity: more hardware, more coordination for legitimate transactions, and sometimes higher fees depending on the blockchain.

For U.S.-based users, an often pragmatic approach is layered: keep a primary Ledger Nano for daily use, a secondary hardware device or multisig for large holdings or long-term storage, and a secure, geographically separated recovery plan for seed material. That pattern distributes risk across devices and physical locations rather than concentrating it in a single seed phrase or device.

Diagram illustrating on-device transaction verification, host software flow, and seed recovery trade-offs

Practical Heuristics: What To Do Next

Here are five decision-useful heuristics I use and recommend to clients and readers:

1) Assume remote compromise is inevitable. Design for it. Keep only an operational balance on hot wallets; store the rest in hardware custody.

2) Treat your seed phrase as the highest-value secret. Never store it digitally, and consider splitting it across secure physical locations rather than using copy-paste backups.

3) Use device verification. Make it a habit to read recipient addresses and amounts on the device screen before approving. If you’re using DeFi or dApps, prefer workflows that let you verify on-device and avoid exposing the seed to browser extensions.

4) Learn one advanced option (multisig or secondary hardware) and test recovery. If you choose multisig, practice a recovery drill: simulate losing one signer and restore with the remaining ones. The exercise uncovers hidden assumptions.

5) Buy devices from authorized channels and keep firmware current. Newer firmware often patches practical attack vectors; updates also add compatibility with evolving Web3 services. The Ledger ecosystem has been integrating more tightly with dApps so you can access DeFi while keeping your seed offline — a practical signal that usability and security are converging.

For those ready to explore hardware custody, the company ecosystem provides authoritative starting points and how-to guides; one user-oriented reference that collects guides and product details is hosted at ledger.

Limits, Open Questions, and What to Watch Next

Hardware wallets have matured, but several open questions and trend signals matter for future risk management:

– Integration with Web3: As Ledger and other wallets add dApp integrations, watch how they preserve on-device verification. Usability wins are valuable only if they do not degrade the “confirm on device” guarantee.

– Post-quantum threats: Quantum-resistant signatures are an active research area. Today’s secure elements are not quantum-proof; keep an eye on standards and hardware that support post-quantum algorithms if and when they become recommended by security bodies.

– Regulatory and legal risks: In the U.S., legal pressures around compelled disclosure or device seizure are still evolving. Understand how local laws around search, seizure, and compelled decryption could intersect with physical custody decisions and consider legal advice if you hold significant assets.

– Supply-chain sophistication: Nation-state or targeted attackers can attempt sophisticated supply-chain attacks. Diversity of procurement and physical inspection protocols reduce but do not eliminate this class of risk.

Most of these issues are open rather than resolved. They’re worth monitoring because technical enhancements and legal change could materially shift what custody strategies are sensible.

FAQ

Do I still need a hardware wallet if I use an exchange with insurance?

Yes, for most individuals in the U.S. exchanges’ insurance and custody arrangements are designed to protect the platform and its customers under specific conditions, but they do not remove counterparty risk. Using a hardware wallet gives you direct control of private keys and removes dependency on an exchange’s solvency, operational security, or policy decisions.

What’s safer: a Ledger Nano or a multisig with multiple devices?

They protect against different risks. A single Ledger Nano reduces remote hack risk and is convenient. Multisig protects against single-point failures (lost device, compromised seed) but adds complexity. For significant holdings, combining hardware wallets with a multisig architecture often offers a better balance of resilience at the cost of more setup and maintenance.

How should I back up my recovery phrase?

Prefer physical backups in secure, geographically separated locations (e.g., safe deposit box, home safe, trusted custodian). Avoid digital copies or photos. Consider metal plates for durability against fire and water. If you split phrases, document the reconstruction protocol clearly and test it without transmitting any secret material digitally.

Can a hardware wallet protect me against phishing?

Partially. Hardware wallets prevent unauthorized signing without physical confirmation, which stops many phishing attacks that rely on remote credential theft. However, sophisticated phishing can still trick users into approving malicious transactions if they do not carefully verify details on-device. User education and disciplined verification remain essential.

How often should I update device firmware?

Install firmware updates after confirming release notes from official sources and ensuring you follow recommended update procedures. Updates close known vulnerabilities and add compatibility, but always follow official guidance to avoid supply-chain confusion or fake update prompts.

Portfolio Tracking, Risk Assessment, and MEV Protection: Choosing the Right DeFi Workflow

Consider a familiar US DeFi situation: you open your wallet before work and discover that your portfolio appears healthier than expected. A token balance has risen, but a lending position is close to liquidation. A swap you submitted last night settled at a worse price than the quote. Meanwhile, a dashboard reports one neat total value that quietly combines volatile assets, debt, pending rewards, and illiquid positions. Nothing has necessarily been hacked. The problem is that the interface has compressed several different risks into one number.

Effective DeFi security therefore begins before a transaction is signed. It requires three connected practices: tracking what the portfolio actually contains, assessing how its exposures can change, and reducing the information leakage that allows hostile or opportunistic transaction ordering. These practices overlap, but they are not interchangeable. A wallet can simulate a transaction without providing full portfolio accounting; a portfolio tracker can show risk without protecting a pending swap from maximal extractable value, or MEV, strategies. The useful question is not which tool is “best,” but which failure mode each workflow addresses.

Wallet interface concept illustrating transaction review and portfolio risk awareness

Why a portfolio balance is not a risk assessment

Portfolio tracking is usually treated as an accounting problem: identify wallet addresses, read on-chain balances, apply market prices, and calculate a total. That is valuable, but incomplete. The same dollar balance can represent very different economic positions. A liquid stablecoin, a governance token in a thin market, collateral deposited into a lending protocol, and a claim on a liquidity pool may all appear beside one another while carrying different exit, smart-contract, and price risks.

A more useful mental model separates at least four dimensions. First is market exposure: how much value depends on the price of an asset, a correlated group of assets, or a volatile collateral ratio. Second is liquidity exposure: how quickly the position can be reduced without materially moving the market. Third is protocol exposure: the possibility that code, an oracle, an administrator, or a bridge fails. Fourth is operational exposure: incorrect approvals, compromised keys, phishing, wrong-chain transactions, and misunderstood contract behavior.

This distinction produces a non-obvious conclusion: diversification by token count is not necessarily diversification by risk. Ten assets may all depend on the same blockchain, stablecoin mechanism, bridge, or liquidity venue. Conversely, two positions may have different token names but share a common liquidation trigger. Tracking should therefore record relationships, not only balances. A lending position, for example, should be viewed alongside its collateral asset, borrowed asset, liquidation threshold, oracle dependency, and available exit liquidity.

Three approaches to DeFi portfolio oversight

Approach one: the spreadsheet or manual ledger

A spreadsheet remains useful for users who want explicit assumptions. It can distinguish principal from rewards, record realized and unrealized gains, and show whether a position is strategic, speculative, or reserved for taxes. For US users, this separation can also make the difference between a useful transaction history and a confusing pile of wallet activity when preparing records for tax reporting. Manual tracking is transparent: you know where the numbers came from.

Its weakness is timeliness and interpretation. On-chain positions change continuously, token prices move, and a manually entered balance can become stale at exactly the moment risk increases. A spreadsheet also struggles with complex positions such as liquidity-provider shares, rebasing assets, vesting claims, or collateral that can be liquidated automatically. It is best used as a long-horizon record and decision journal, not as the sole control layer for time-sensitive transactions.

Approach two: an automated portfolio dashboard

Automated trackers reduce the cost of observation. They can aggregate addresses and networks, estimate market values, identify token balances, and reveal concentrations that are easy to miss when each chain is viewed separately. This is particularly useful for an active DeFi user whose apparent diversification is spread across Ethereum, layer-two networks, and other compatible chains.

Automation, however, does not remove the need for judgment. A dashboard may rely on price feeds that are delayed, unavailable, or misleading for illiquid assets. It may classify a receipt token incorrectly, omit a debt position, or show a nominal value for an asset that cannot be sold at that price in realistic size. Cross-chain data can also create a false sense of one unified portfolio when settlement, bridge, and counterparty risks remain separate.

The practical rule is to treat automated valuation as an estimate, not a liquidation guarantee. Ask what price source is being used, whether debt and accrued obligations are included, and how the system handles assets with limited liquidity. The more complex the position, the more important it becomes to inspect the underlying protocol rather than relying on a summarized label.

Approach three: wallet-native review and transaction simulation

A security-focused wallet addresses a different part of the problem: the decision immediately before authorization. Transaction simulation attempts to show the expected state change before the transaction is broadcast. Instead of asking only, “What fee am I paying?” the user can ask, “Which assets will leave my wallet, which approvals will change, and what will I receive if the transaction behaves as represented?” When the simulation is understandable, it can expose an unintended token transfer or an approval broader than the user intended.

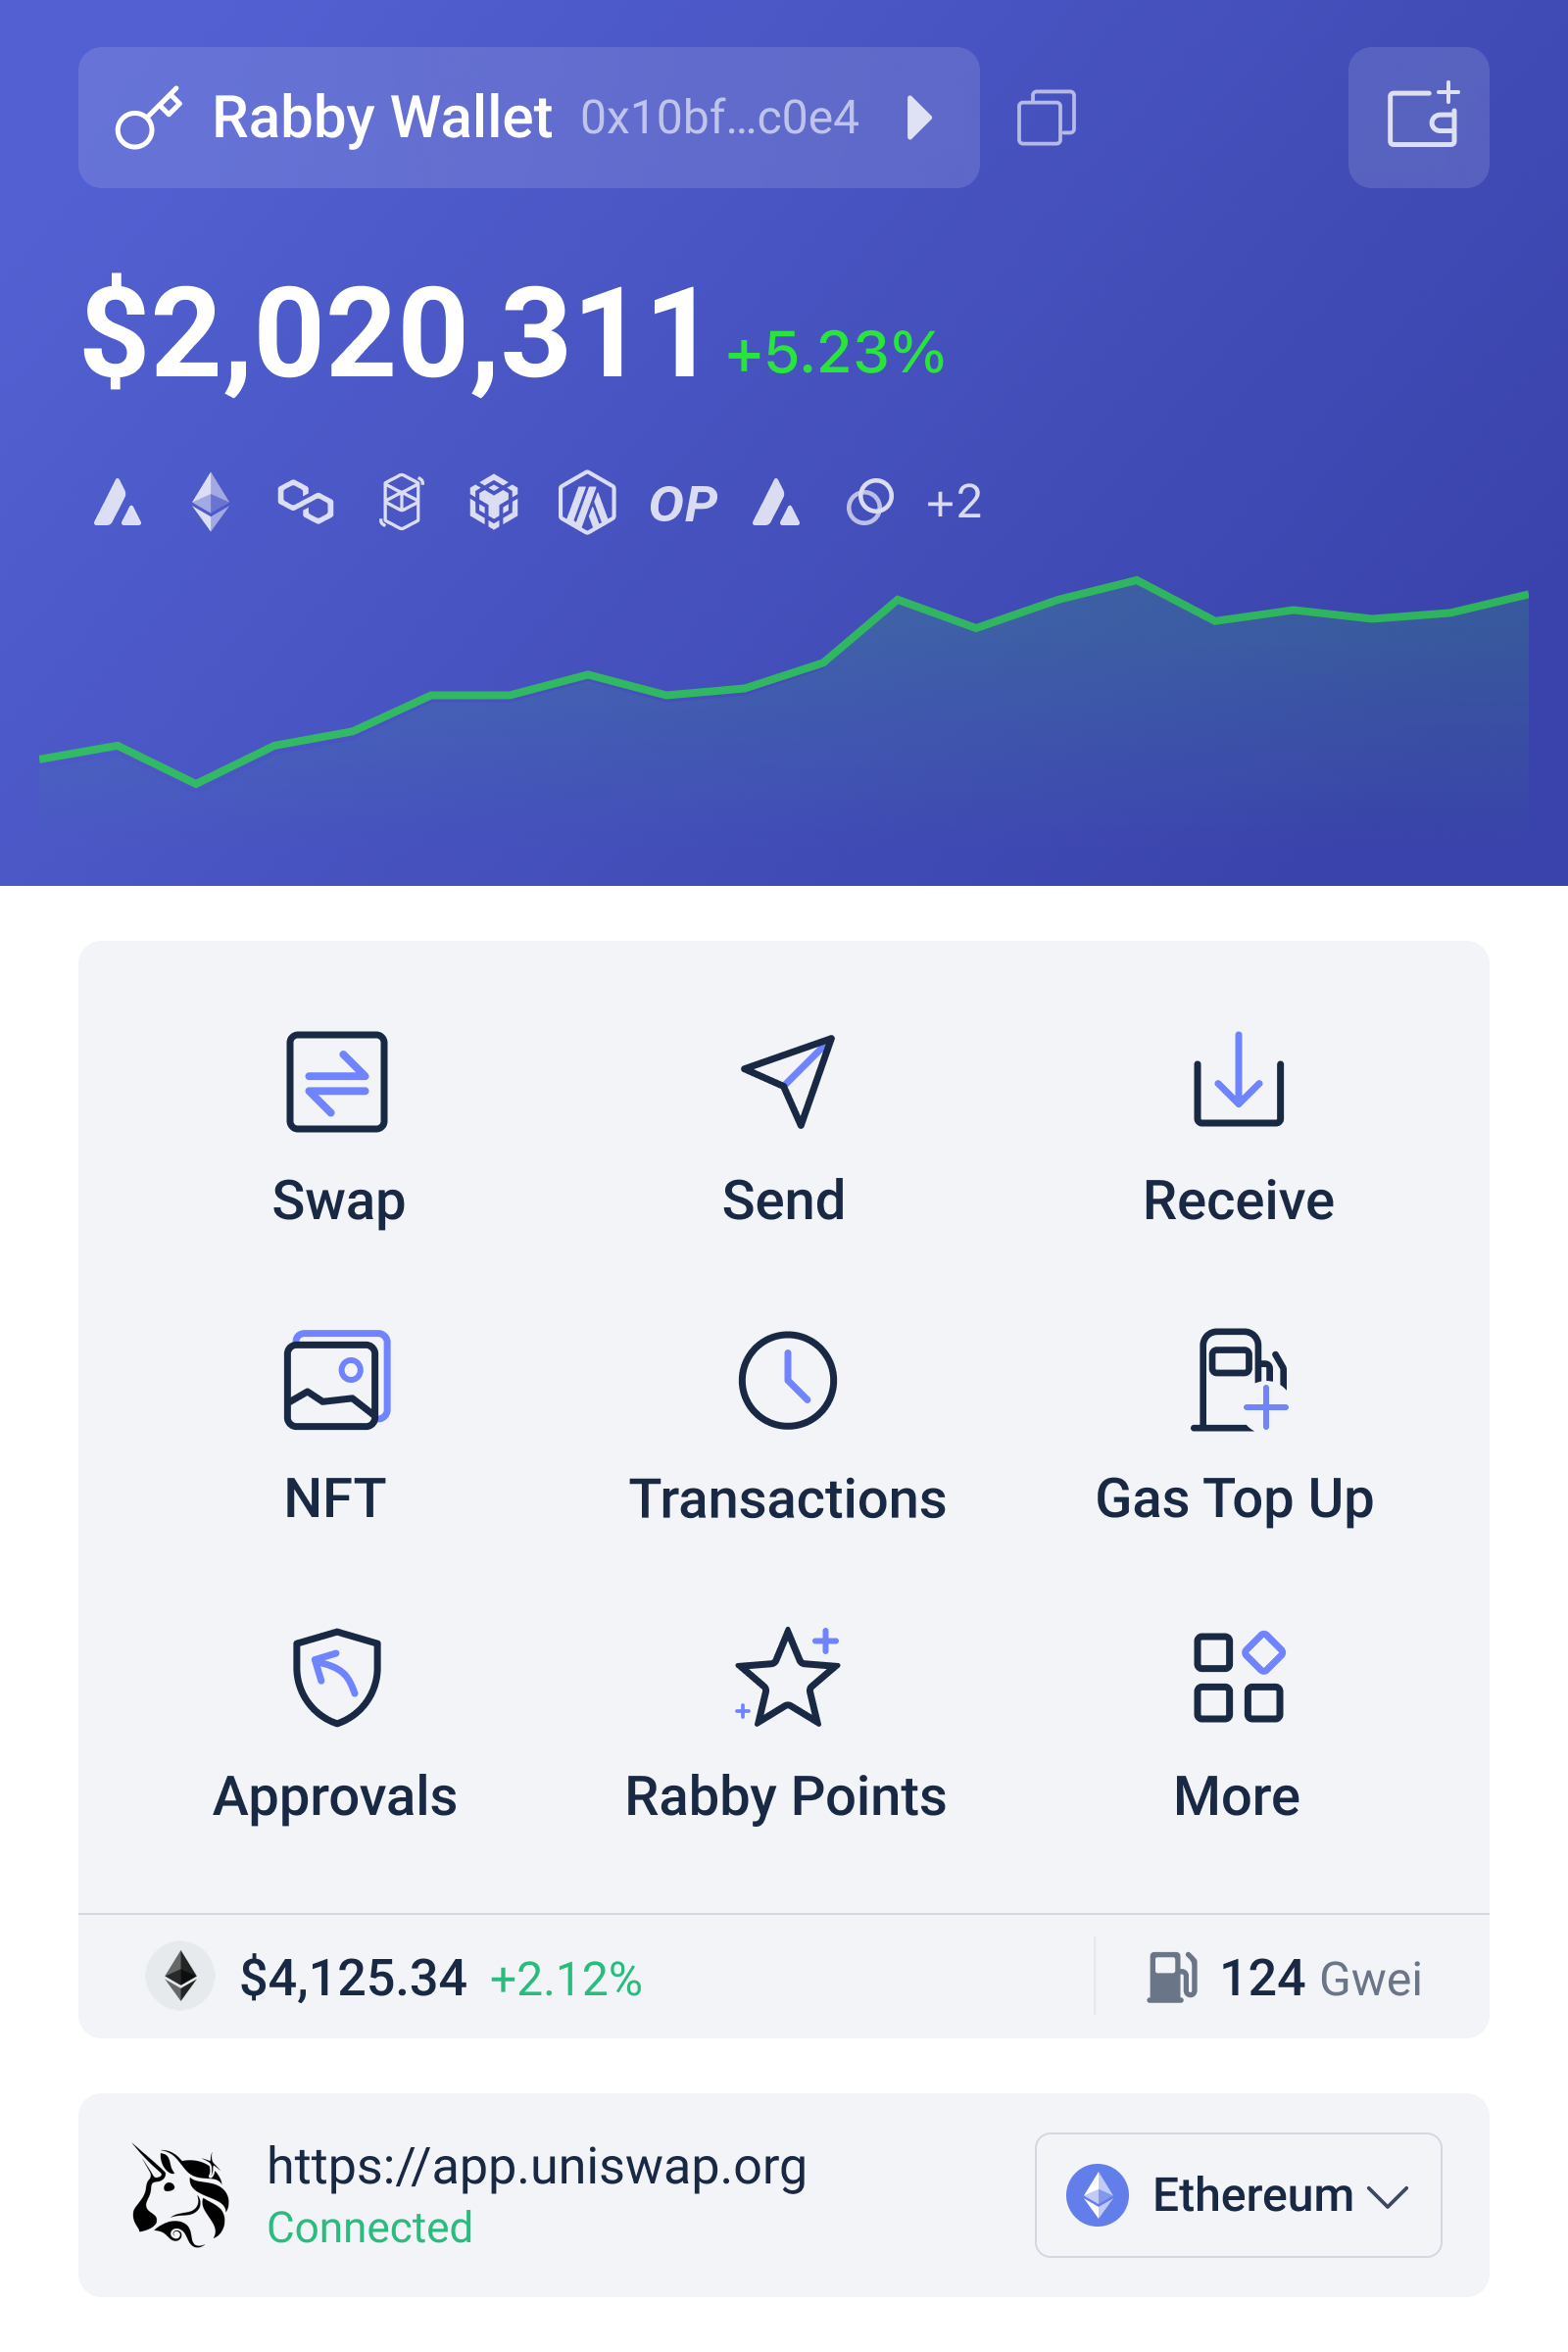
This approach is especially valuable against a common misconception: a transaction can be technically valid and still be economically dangerous. A malicious or compromised website may generate a transaction that the blockchain accepts while the user misunderstands its effects. Simulation cannot prove that a contract is safe, nor can it guarantee that the final on-chain state will match an estimate under all market conditions. It is a pre-execution control, not an audit and not a substitute for careful contract and permission review. Users seeking this type of workflow may find a rabby wallet useful to evaluate alongside their existing tracking tools, particularly when transaction interpretation is as important as balance display.

Where MEV protection fits

Maximal extractable value refers to value obtained by controlling or influencing transaction ordering, usually by observing pending transactions and arranging transactions around them. The most recognizable example is a large swap that reveals its intended trade to the public transaction queue. Other transactions may be placed before and after it, worsening execution for the original trader or capturing price movement created by the trade. Not every unfavorable fill is MEV: ordinary volatility, shallow liquidity, routing choices, and fees can produce similar outcomes.

MEV protection works by changing the information and ordering environment. A transaction may be sent through a private submission path, routed through an execution design that reduces exposure, or protected with limits such as slippage tolerance. Each method involves trade-offs. Private routing can reduce public visibility, but the user must trust the intermediary or relay and accept that availability may differ by network. Tight slippage limits can reduce losses from price movement and sandwiching, but they also increase the chance that a transaction fails. A larger tolerance improves execution probability while giving adverse price movement more room.

That trade-off shows why “MEV protection” is not a binary property. Protection depends on the transaction type, chain, route, liquidity, timing, and submission method. A small swap in a deep market has a different exposure from a large swap in a thin pool. A limit order, an aggregator route, and a direct automated-market-maker trade create different information footprints. The strongest workflow combines simulation, sensible slippage settings, review of the recipient and spender, and an execution path suited to the transaction.

A reusable decision framework

Before signing, separate three questions that are often collapsed into one screen. The first is portfolio question: what does this transaction do to my overall exposure? The second is contract question: what exact state change am I authorizing? The third is market-structure question: who can observe, reorder, or react to this transaction before it settles?

For portfolio exposure, identify whether the transaction increases leverage, concentration, bridge dependence, or reliance on a single protocol. For contract exposure, inspect approvals, recipients, permissions, and the difference between a one-time spend and an effectively unlimited allowance. For market-structure exposure, consider trade size relative to liquidity, slippage tolerance, whether the transaction is publicly visible, and whether failure would be preferable to execution at a worse price.

A simple risk register can make this operational. Label each position by market, liquidity, protocol, and operational risk, then mark whether the exposure is direct or shared with another position. Review the highest-impact risks first. A wallet holding a modest balance but carrying a large approval to an unfamiliar contract may deserve more immediate attention than a larger balance held without active permissions. This is a sharper use of attention than checking total portfolio value alone.

Limits, uncertainty, and what to watch next

No interface can eliminate smart-contract risk, oracle failure, validator behavior, private-relay dependence, or user error. Simulation is conditional on the state observed when it runs; markets can move between simulation, submission, and settlement. Portfolio values are conditional on available liquidity. MEV defenses can reduce one attack surface while introducing a different trust or availability assumption. These are boundary conditions, not reasons to abandon the tools. They are reasons to understand what each control actually guarantees.

The near-term direction of DeFi security is likely to be more integrated decision support, provided the underlying data and execution assumptions remain visible. A useful system would connect portfolio concentration with transaction simulation and execution risk: for example, warning not only that a swap may fail, but that it would leave a user excessively dependent on one volatile asset or reduce collateral safety. Whether such systems become genuinely reliable will depend on better treatment of complex positions, cross-chain context, and uncertainty rather than on more attractive dashboards.

Frequently asked questions

Is portfolio tracking enough to protect a DeFi user?

No. Tracking helps explain balances and exposures, but it does not necessarily inspect contract permissions, simulate state changes, or protect pending transactions from adverse ordering. It should be combined with transaction review and appropriate execution controls.

Does transaction simulation guarantee that a transaction is safe?

No. Simulation estimates what a transaction may do under a particular blockchain state. It can reveal unexpected transfers, approvals, or failures, but it cannot establish that the contract is trustworthy or that market conditions will remain unchanged before settlement.

How should a user choose between private routing and strict slippage limits?

They address related but different risks. Private routing can reduce public visibility, while strict slippage limits constrain the price damage the user will accept. The right choice depends on network support, route liquidity, transaction size, and whether a failed transaction is preferable to uncertain execution.

The central lesson is straightforward but easy to overlook: a DeFi portfolio is not merely a collection of balances. It is a set of changing claims, permissions, dependencies, and market interactions. Tracking explains what is held, simulation clarifies what a signature may change, and MEV-aware execution addresses how the transaction enters a competitive market. Used together—and interpreted with their limits in view—they turn a wallet from a passive display into a more disciplined risk-control process.

Dust Attacks and Wallet Privacy: How Tangem’s Non-Custodial Design Protects Your Identity

A cryptocurrency holder receives a small deposit—sometimes a fraction of a cent—to a wallet address they use regularly. The amount is negligible, but the purpose is reconnaissance. A chain analyst, competitor, or surveillance operation has sent what is called a “dust attack,” a test to see if the recipient will move the funds and expose transaction patterns, address clustering, and spending behavior. The victim may consolidate dust into a larger transaction, accidentally linking multiple holdings and revealing activity across time and wallet implementations. This attack works because most users treat their wallet as a simple interface rather than understanding the relationship between custody, privacy, and transaction visibility.

Non-custodial hardware wallets present a fundamentally different privacy model than centralized exchanges or custodial platforms. When a service holds private keys on behalf of users, it sees every transaction, knows every address, and maintains internal records that can be requested, subpoenaed, or compromised. A non-custodial wallet like Tangem inverts that relationship: the user controls the private keys entirely, while the service never sees the secrets, addresses, or transaction history. That separation is the foundation of privacy. But a wallet that stores keys securely does not automatically prevent a user from exposing themselves through careless address reuse, obvious consolidation patterns, or connection to services that already know their identity. Understanding how Tangem’s design prevents certain attack surfaces while requiring active privacy discipline from users is essential for anyone trying to maintain actual ownership of cryptocurrency.

A Tangem card and ring hardware wallet showing NFC-based interaction with a mobile application for secure offline private key storage

The dust attack as a privacy diagnostic

A dust attack exploits a behavioral reality: most people do not want to leave small amounts in wallets unused. When they receive unexpected deposits, they eventually move them or consolidate them with other funds. This consolidation is traceable. If a user has received dust at address A, and address B in the same wallet receives a legitimate payment, an observer can watch for a transaction that spends outputs from both addresses in a single consolidation event. That transaction reveals that A and B are controlled by the same entity. Repeat this process across dozens of dust deposits and thousands of transactions, and a clear map of holdings and behavior emerges.

The attack is particularly effective against users who rely on custodial services or exchange wallets. If a user maintains a wallet on an exchange platform and receives dust, the exchange can see the incoming transaction immediately, note the address, track any consolidation attempt, and maintain records linking the deposit to the user’s account and identity. The exchange’s internal database becomes a chain-of-custody record for every movement the user makes. A regulatory request or accidental breach can then expose years of transaction history in one event.

A non-custodial wallet changes this dynamic because the service provider never sees the addresses or transactions. When using a non-custodial wallet like Tangem, dust arrives at an address that only the cardholder knows and controls. The wallet provider cannot log it, cannot alert the user to consolidation risk, and cannot be compelled to produce transaction records because none were created in their systems. This does not make dust disappear from the blockchain—the transaction is still public—but it breaks one critical chain: the connection between the user’s identity and the cryptocurrency addresses they control.

However, the user must still choose how to respond when they discover dust. If they immediately consolidate it with other outputs in a transparent way, the blockchain analysis remains possible. If they spend it carelessly to a service that identifies them (an exchange, a tracked merchant, or a payment processor), they have reconnected the link themselves. The wallet’s non-custodial design prevents the service provider from being the weak point; it cannot prevent the user from becoming one through their own choices.

Why key custody determines the privacy boundary

The most fundamental privacy distinction in cryptocurrency is who holds the private keys. If a service holds the keys, it has cryptographic proof that it can generate and sign transactions, meaning it has complete access to the funds and can observe or intercept every movement. It must also defend those keys against internal threats (rogue employees), external attackers (hackers targeting the service), and legal demands. If the user holds the keys, the service has no such access, no such liability, and no such records to produce. That asymmetry defines everything about privacy and security that follows.

Tangem wallet architecture implements this boundary through a secure element—a specialized cryptographic chip that generates private keys offline and stores them in encrypted, tamper-resistant memory. The card or ring never exposes the key material even to the mobile phone it connects to. When a transaction must be signed, the user brings the card near their phone using NFC, and the secure element performs the cryptographic operation internally, returning only the signature. The phone sees the transaction data and the signature, but never the private key. This is categorically different from a wallet application that stores keys in a phone’s memory, even if encrypted, because the key generation and signing operations occur in hardware that the user controls, not in software that their phone’s operating system or any application could potentially intercept.

This design immediately eliminates several attack surfaces. A compromised phone cannot extract the key. Malware cannot sign unauthorized transactions because the secure element requires physical proximity for signing. A backup of the phone’s data will not reveal the key. A thief who steals the phone cannot drain the wallet without the card. The user’s cryptocurrency remains secure even if they lose physical custody of the device they normally use to check balances and create transactions.

The custodial comparison is stark. An exchange, even one with security certifications, maintains private keys in its infrastructure. That infrastructure may use hardware security modules, cold storage, and access controls, but it is still centralized in one organization’s hands. A user who deposits funds to an exchange has transferred key custody to that organization. They can then access those funds only with permission—a password, two-factor authentication, and agreement to the exchange’s terms of service. If the exchange is hacked, goes bankrupt, or refuses withdrawal requests, the user has no cryptographic recourse. The funds are simply gone or inaccessible.

Address reuse and privacy costs in transparent blockchains

Bitcoin, Ethereum, and most major cryptocurrency networks record all transactions publicly and permanently. This means address reuse—using the same public address to receive multiple payments over time—creates a persistent, observable link between those payments. If Alice has received ten separate payments to address X, and then spends them together, it is mathematically clear that the same entity controlled all ten payments. An observer analyzing the blockchain can cluster related addresses and infer holdings, spending patterns, and even personal identity if the user has ever connected an address to a known service or person.

Tangem addresses this through deterministic key derivation, allowing users to generate a nearly unlimited number of distinct addresses from a single card. Each address can be used for a single receiving context or person, preventing consolidation patterns from being obvious. When a user later needs to spend, they can choose which addresses to consolidate based on privacy and efficiency trade-offs rather than being forced to use whatever address had the lowest balance. This capability exists in many wallets, but it matters more when the wallet is non-custodial because the user has no intermediary filtering or analyzing the choice. The service provider cannot intercede, cannot log preferences, and cannot create correlations.

However, this strength also reveals a user discipline requirement. Generating diverse addresses is meaningless if the user then spends them carelessly. For example, if Alice uses address X1 to receive payment from her employer, and address X2 to receive payment from a friend, and then spends both X1 and X2 together, the blockchain still shows consolidation. An observer cannot see that one payment was employment income and the other was personal, but they can see that the same entity controlled both. More importantly, if the employer or friend has any visibility into the blockchain (many services now provide this), they can observe that the payment they sent was later combined with other funds, potentially revealing Alice’s spending patterns to people who otherwise would not know them.

The real privacy lesson is that address reuse and consolidation are visible whether or not the wallet is custodial. The custodial difference is that a centralized service would know the connection anyway. A non-custodial design simply refuses to be a weak point. If the user then re-creates the link through their own behavior, that is a different problem—one that requires education and discipline, not a better wallet.

Seedless backups and the recovery phrase trade-off

Traditional hardware wallets ask users to write down a recovery phrase—typically 12 or 24 words—when they first set up the device. This phrase is the master secret from which all private keys are derived. If the hardware wallet is lost or damaged, the recovery phrase can be imported into another wallet to restore all funds. The assumption is that users will store this phrase in a physically secure location, never photograph it, and never enter it into any computer. In practice, many users violate these rules.

Tangem eliminates the recovery phrase entirely by offering what is called a “seedless” backup system. Instead of writing down words, users can create one or more additional backup cards. If the primary card is lost, the backup card can restore the wallet. The backup card is itself a secure element with the same tamper resistance and isolation as the primary card. This removes the most dangerous vulnerability: a text file, notebook, or photographed phrase that a thief, family member, or housekeeper could discover.

The backup card approach introduces a different risk: managing multiple physical objects. A user with two cards must decide which to use daily, where to store the backup, and how to verify that it actually works if a recovery becomes necessary. Some users may find multiple cards more secure than a written phrase; others will find them more burdensome. The trade-off is worth understanding explicitly. A recovery phrase written carefully and stored securely might be extremely safe; a backup card stored carelessly in a desk drawer is not. Conversely, a recovery phrase that someone enters into a cloud backup application or a text editor is catastrophically vulnerable, while multiple backup cards reduce that particular vector.

The option to create backup cards also affects privacy in one subtle way. If a user creates a backup card and stores it with someone else (a family member, a safe deposit box at a bank, or a escrow service), that party has access to the wallet’s recovery mechanism. They cannot see individual transactions or addresses unless the user reveals them, but they can potentially restore the wallet and access all funds if the primary card is lost and the user is unavailable. This is a trust and custody relationship, different from the primary card’s isolation but worth considering in security planning.

NFC-based signing and the absence of browser extension risk

Most cryptocurrency users interact with decentralized applications through a browser extension wallet like MetaMask or Phantom. The extension has constant access to the browser, can see the websites the user visits, and can intercept transactions before they are signed. A malicious website can trick the extension into signing transactions, sometimes simply by requesting a signature for what appears to be an innocuous message. A compromised or malicious extension can drain wallets by signing unauthorized transactions or by stealing private keys if the extension stores them directly.

Tangem removes the browser extension from the signing chain entirely. A decentralized application connects to the wallet through a standard protocol (WalletConnect or similar) that sends transaction data to the mobile application, never to a browser extension. The user views the transaction details in the Tangem app, confirms them by bringing the card near the phone, and the secure element signs the transaction. The browser never sees the private key, never participates in the signing process, and cannot intercept or redirect funds. This is a substantial reduction in attack surface.

The trade-off is speed and convenience. Signing through an extension is nearly instantaneous once the request appears. Signing with a hardware card requires the user to have the card physically present and to perform an NFC interaction, which takes a few seconds and requires awareness of what is being signed. For frequent transactions, this is slower. For high-value or infrequent transactions, the friction is actually beneficial because it encourages the user to read the transaction details before approving.

The NFC-based confirmation model also reveals another privacy dimension. Unlike a browser extension that might sign in the background or respond to automated requests, the Tangem card requires user presence and intention. This does not prevent a user from being tricked into signing a harmful transaction by a deceptive interface, but it does require intentional action rather than passive background processing. A scammer cannot drain the wallet through a vulnerability in the extension layer or through silent authorization requests.

Decentralized node selection and transaction broadcasting privacy

When a transaction is signed and ready to broadcast, the question becomes: which network node receives it, and can that node or others observe identifying information about the sender? If a user’s wallet directly connects to their own node, and that node is running on their own infrastructure or through a trusted privacy-focused service provider, then the broadcast is routable through layers that do not see the IP address or do not correlate transactions with user identity. If the wallet uses a public node provider, the provider’s servers see the IP address, the transaction data, and can correlate multiple transactions if they come from the same IP over time.

Tangem’s non-custodial design does not inherently solve this problem because it is a network-layer issue, not a key-custody issue. Whether the wallet is custodial or non-custodial, the transaction still goes somewhere to be broadcast. What the design does is ensure that the wallet provider itself is not the intermediary. Users can configure which node providers the wallet connects to, can choose to route through Tor or a VPN, and can use their own node if they operate one. The wallet does not have a business interest in observing these details because it does not maintain a database of user transactions.

Compare this to a custodial exchange. The exchange receives the transaction from the user, broadcasts it from its own infrastructure, and maintains internal records of when the transaction was submitted, what the network fee was, and whether it succeeded. The exchange’s logs contain a detailed history of the user’s transaction activity. A regulatory request or breach of the exchange’s systems exposes this history all at once. A non-custodial wallet provider has no equivalent logs to produce because the transaction was created and broadcast entirely by the user’s device, not submitted to the provider’s systems.

Multi-chain support and privacy complexity across networks

Tangem supports thousands of cryptocurrencies across dozens of blockchains: Bitcoin, Ethereum, Litecoin, Polygon, Solana, and thousands of ERC-20 tokens among them. This convenience means a user can hold multiple assets without multiple wallets or recovery phrases. It also means a user might consolidate holdings across multiple networks without understanding the privacy implications of each network’s transaction model.

Bitcoin, for example, exposes transaction amounts, inputs, and outputs publicly. Privacy techniques like PayJoin or coin control can help, but the default transaction is transparent. Ethereum shows similar information: the sending address, receiving address, amount transferred, and all contract interactions are visible to everyone. Some tokens operate on privacy-focused networks like Monero, but most do not. A Tangem wallet that holds both Bitcoin and Ethereum can execute transactions on both networks, but a user cannot assume that the privacy properties are equivalent. Moving funds between networks or consolidating holdings across networks can create chain-analysis opportunities if an observer is watching both blockchains.

The wallet itself handles this correctly by keeping the keys isolated and the signing process secure. The problem belongs to the user: understanding which assets have which privacy properties, which consolidation patterns are observable, and whether any of the addresses or transactions can be linked to known identity information. A secure crypto storage solution prevents the service provider from being the weak point, but it does not prevent the user from being careless. Tangem’s role is to ensure the keys are protected and the wallet provider has no visibility into transactions. The rest is user behavior.

The practical privacy hierarchy: what actually matters

When evaluating wallet privacy, users should think in layers. The first layer is key custody: who holds the private keys. A non-custodial design like Tangem’s is substantially better than custodial alternatives because the service provider cannot see transactions, maintain records, or be a target for regulatory demands. This is foundational and worth the effort to maintain. The second layer is key security: can the keys be extracted or used without authorization. Hardware-based signing with offline key generation addresses this. The third layer is address and transaction management: does the wallet encourage diverse addresses, careful consolidation, and appropriate privacy techniques for each network. The fourth layer is network privacy: can an observer identify the IP address, the timing of transactions, or the connection to wallets. The fifth layer is user behavior: does the user understand these issues and avoid obvious mistakes like reusing addresses across identified and unidentified contexts.

Tangem excels at the first two layers. It provides excellent tools for the third layer through address derivation and deterministic key generation. It leaves the fourth and fifth layers to the user. This is appropriate because network privacy and behavioral discipline are not problems that a wallet can solve unilaterally. A user can undo all of a wallet’s privacy benefits by consolidating dust carelessly or by moving funds to a service that already knows their identity. The wallet’s contribution is to ensure that it never becomes a choke point where third parties are forced into visibility.

For anyone concerned about cryptocurrency privacy and ownership, the distinction between custodial and non-custodial is the first and most important decision. All the privacy techniques, secure signing processes, and address management tools follow from that choice. Tangem makes that choice concrete by implementing a non-custodial design with offline key generation, hardware-based security, and no service-side access to private keys or transaction history. You can explore a secure hardware wallet for crypto storage to understand the practical implementation, but the underlying principle is simple: if the wallet provider cannot see the transaction, they cannot be forced to reveal it, and they cannot inadvertently leak it through poor security or negligent practices.

Frequently asked questions

Can dust attacks harm my cryptocurrency if I use Tangem?

Dust attacks cannot drain funds because Tangem is non-custodial—only you can sign transactions. However, the dust amount will still appear on the blockchain. The real risk is that you consolidate the dust with other funds in an obvious way, linking addresses that should have remained separate. Tangem helps by allowing you to generate diverse addresses and control consolidation carefully, but the blockchain visibility remains unchanged.

Why does Tangem not use a recovery phrase like other hardware wallets?

The seedless backup system uses additional hardware cards instead of written words. This eliminates the risk that someone will photograph, digitize, or discover your recovery phrase. However, you then need to manage and protect multiple physical cards. Both approaches have trade-offs; neither is universally superior in every situation.

How does Tangem protect my privacy from the wallet provider?

Tangem never sees your private keys, addresses, or transactions because signing happens entirely on the secure element chip in the card. No transaction records are created by the provider. This is fundamentally different from custodial wallets where the service maintains complete records of your activity. However, your privacy still depends on which nodes you broadcast to and whether you reuse addresses in ways that link your transactions together.

What Makes a Privacy Wallet Private? Understanding Monero, Litecoin MWEB, and Bitcoin in One App

What does it really mean for a wallet to protect privacy: hiding the amount, hiding the sender, hiding the recipient, or simply avoiding a company’s data collection? Those are different problems, and treating them as one is the fastest way to misunderstand a privacy wallet. For users in the United States who move between Monero, Bitcoin, Litecoin, and other assets, privacy depends on several layers working together: the blockchain’s design, the wallet’s handling of keys, the network connection, and the user’s own habits.

A multi-currency wallet is therefore not automatically a multi-privacy wallet. Monero has privacy built into its transaction system, while Bitcoin privacy depends more heavily on optional techniques such as coin control, PayJoin, and Silent Payments. Litecoin’s MimbleWimble Extension Blocks, or MWEB, provide an optional privacy layer rather than changing every Litecoin transaction by default. The useful question is not whether a wallet carries a “private” label, but which information each asset and feature actually conceals.

Mobile cryptocurrency wallet interface illustrating multi-asset management and privacy controls

Privacy is a stack, not a switch

Consider four layers. First is transaction privacy: whether observers can connect addresses, amounts, and payment relationships on a public ledger. Second is key custody: who controls the private keys that authorize spending. Third is device privacy: whether someone with access to a phone or computer can read wallet data. Fourth is network privacy: whether an internet provider, node operator, or other observer can associate an IP address with wallet activity.

These layers can fail independently. A non-custodial wallet can give a user control of the keys while still revealing network metadata if connections are made carelessly. Conversely, routing traffic through privacy-preserving infrastructure cannot make a transparent blockchain private. This distinction is especially important in the US, where exchange records, payment processors, and ordinary financial accounts may create identity links outside the blockchain itself. On-chain privacy cannot erase information already disclosed to a regulated service or merchant.

Cake Wallet’s architecture addresses several of these operational layers. It is open source and non-custodial, meaning private keys remain under the user’s control rather than being transmitted to or stored on the wallet’s servers. Wallet data is protected with device-level security hardware, such as Secure Enclave on iOS or TPM-based protections on Android, with local access controlled through a PIN or biometric authentication. The wallet also describes a zero-telemetry approach: transaction histories, IP addresses, and device identifiers are not tracked or logged by its developers.

Those are meaningful safeguards, but they are not substitutes for backup discipline. A lost phone, forgotten PIN, exposed recovery phrase, malicious screen-recording application, or careless clipboard action can still compromise funds or privacy. Biometrics make routine access convenient, while the recovery phrase remains the deeper authority. Users should treat that phrase as a high-value secret, store it offline, and avoid photographing or placing it in cloud storage.

Why a Monero wallet behaves differently

Monero is often the clearest example of privacy as a protocol mechanism rather than a menu option. Its design seeks to obscure transaction relationships through features that protect sender information, recipient information, and transaction amounts. In a wallet context, subaddresses add another useful layer: a user can create distinct receiving destinations for different people or purposes, reducing the need to reuse one public address as a universal identifier.

A practical example would be separating freelance income, household payments, and donations with different Monero subaddresses. That does not make the user invisible, and it does not prevent an outside party from learning information voluntarily shared with a counterparty. It does, however, make simple address-based profiling less informative. Cake Wallet also supports background synchronization and keeps the private view key on the device. The latter matters because a view key can reveal transaction history without necessarily granting spending authority; keeping it local reduces the number of places where sensitive financial information can travel.

The limitation is that wallet privacy still depends on the surrounding workflow. If a user buys Monero through a service that records identity, sends it to a known personal address, and then publicly discusses the payment, the protocol’s protections cannot undo those disclosures. Monero can reduce blockchain-level exposure, but it is not a cloak against every form of financial surveillance, social inference, or endpoint compromise.

Litecoin MWEB: optional privacy with a boundary

For Litecoin users, MWEB is best understood as a separate privacy path rather than a universal property of Litecoin. MimbleWimble Extension Blocks allow users to move Litecoin into an optional extension-block environment where transaction details can receive stronger protection. The key word is optional. A transaction that remains on Litecoin’s ordinary transparent chain does not gain MWEB’s privacy characteristics merely because the wallet supports them.

This creates a decision point that is easy to miss in a simplified wallet interface: the user must understand whether funds are entering, leaving, or remaining within the privacy-enabled section. There may also be practical considerations around compatibility, liquidity, and whether a counterparty or service supports the relevant transaction path. For a user who values Litecoin’s payment ecosystem but wants a more private transfer in suitable circumstances, MWEB can be useful. It should not be described as making every Litecoin balance private by default.

The broader lesson applies across cryptocurrencies. Privacy features often create “privacy sets”—groups of transactions that resemble one another—rather than perfect isolation. The more consistently a feature is used and the more compatible the surrounding ecosystem becomes, the stronger its practical privacy may be. Sporadic use, unusual timing, or immediate movement between identifiable services can weaken the benefit through contextual clues.

Bitcoin privacy is largely about transaction construction

Bitcoin illustrates a different model. The ledger is transparent, so privacy improvements often depend on how a transaction is assembled and how addresses are used. Specific UTXO coin control lets users choose which unspent outputs are spent together. That matters because combining outputs can create an inference that they belong to the same owner. Coin control is therefore not merely an advanced accounting feature; it is a way to avoid unnecessary information leakage.

PayJoin v2 changes the structure of a payment by allowing payer and payee inputs to appear in the same transaction, making common ownership assumptions less reliable. Silent Payments address a different problem: they allow a recipient to publish a reusable payment identifier while generating distinct on-chain receiving addresses. Transaction batching can reduce fees and data footprint for senders managing multiple payments, although it is primarily an efficiency technique and should not be mistaken for comprehensive anonymity.

These tools require more user awareness than a privacy protocol that operates automatically. A user who carefully applies coin control but repeatedly sends funds to a known exchange account still creates an external identity link. A wallet can expose the controls, but it cannot decide the user’s risk model. For beginners, the decision-useful rule is simple: avoid address reuse, do not casually merge unrelated funds, and learn what a feature changes before assuming it hides everything.

Network privacy, swaps, and the convenience trade-off

Privacy can also leak before a transaction reaches a blockchain. A wallet may connect to a node that sees an IP address, request patterns, or synchronization behavior. Tor-only mode, I2P proxy support, and custom node connections address this network layer by reducing dependence on a single ordinary internet path. They can improve privacy, but they may also add setup complexity, slower synchronization, or availability trade-offs. A private route is useful only if the user can operate it reliably and verify that the configuration is actually active.

Built-in swaps introduce another boundary. Moving directly between assets such as BTC, XMR, and ETH is convenient and can reduce the need to send funds through a centralized exchange account. Cross-chain swaps use NEAR Intents to route requests among multiple market makers without relying on a centralized intermediary for the routing process. Yet decentralized routing does not mean every participant, quote, fee, compliance rule, or settlement path is invisible. Users should review rates, network fees, minimums, and the information required by any market maker involved.

For readers comparing products, the cake wallet model is most usefully evaluated as a combination of custody control, local security, network options, and asset-specific privacy tools. Its broad support includes Monero, Bitcoin, Litecoin, Ethereum, Zcash, Solana, Nano, Haven, ERC-20 tokens, and stablecoins. That breadth is practical for portfolio management, but it also means privacy expectations must be assessed separately for each asset instead of inherited from the strongest one.

Security choices that matter in daily use

Hardware wallet integration can move signing authority away from a general-purpose phone or laptop. Support for Ledger devices and the air-gapped Cupcake hardware wallet solution is relevant for users holding larger balances or treating a mobile device as an interface rather than a vault. Hardware reduces certain attack surfaces; it does not protect against a fraudulent address displayed before signing, a compromised recovery process, or a user approving a transaction without checking its details.

Zcash provides another instructive example. Mandatory shielding in the wallet means outgoing transactions originate from shielded addresses by default, helping prevent accidental exposure through transparent addresses. But migration has a known limitation: Zashi seed phrases are not compatible with a newly created Cake ZEC wallet because of differences in change-address handling. Funds therefore need to be transferred manually. Migration procedures should always be tested with a small amount first, particularly when moving between wallets with different address and change conventions.

There is no single “best privacy wallet” independent of use case. A reasonable framework is to ask five questions: Which asset am I using? What does its protocol hide by default? What optional features must I activate or understand? Who can observe my network connection? Which parts of my identity are already exposed through exchanges, merchants, or social context? The answers are more informative than a generic privacy score.

FAQ

Is a Monero wallet private by default?

Monero provides protocol-level privacy protections, but “private” does not mean untraceable in every circumstance. Wallet backups, device security, exchange records, IP exposure, and information voluntarily shared with counterparties still matter. Subaddresses and privacy-focused network settings can improve the overall position.

Does Litecoin support privacy in the same way as Monero?

No. Litecoin’s MWEB is an optional privacy layer, while Monero’s privacy mechanisms are integrated into its transaction design. Litecoin users must understand when funds are using MWEB and whether the destination or service supports that path.

What is the most important privacy habit for Bitcoin users?

Start by avoiding unnecessary address reuse and learn to separate unrelated funds. Coin control, PayJoin, Silent Payments, and careful transaction construction can help, but they work best when paired with disciplined handling of exchanges, nodes, and receiving addresses.

The most durable mental model is this: a privacy wallet is not a magic eraser for financial history. It is a set of mechanisms that can reduce exposure at different points—on the device, across the network, and on the ledger. If users match each tool to the information it actually protects, they can make more defensible choices about Monero, Litecoin, Bitcoin, and the compromises that come with using all three.

Validator Management, dApp Connectivity, and the Real Role of a Solana Browser Extension

The counterintuitive truth about staking Solana through a browser extension is that the extension does not “run” your validator relationship. It acts more like a controlled signing interface: it helps a wallet communicate with decentralized applications, displays transaction details, and asks you to authorize specific actions. The validator, the Solana network, and the application remain separate parts of the system. Understanding that separation is more useful than treating a wallet extension as a magic staking button.

That distinction matters for US users who want to stake SOL from a familiar browser. A polished interface can reduce friction, but it cannot eliminate validator risk, smart-contract risk, network conditions, or the responsibility of protecting wallet credentials. Recent Solflare project messaging presents the wallet as a way to manage Solana transactions and wallet activity through a more accessible experience. That is relevant context, but “easy to use” should not be confused with “risk-free.”

What validator management actually involves

On Solana, staking generally means assigning SOL to a stake account and delegating that stake to a validator. The validator participates in processing and confirming network activity. In return, delegated stake may earn rewards, subject to network rules, validator performance, commission, and the timing of activation or withdrawal processes. The wallet does not create those rewards. It helps the user submit and authorize the instructions that interact with the network.

A useful mental model is to separate four questions. First, who controls the private key? Second, what transaction is being signed? Third, which validator receives the delegation? Fourth, what happens if the validator performs poorly, charges a high commission, changes its operating profile, or becomes unavailable? A browser extension mainly addresses the first two questions and provides an interface for the third. It cannot guarantee the answer to the fourth.

This corrects a common misconception: staking is not equivalent to sending SOL to a company that promises interest. In non-custodial staking, the wallet holder normally retains control of the signing key, while the stake delegation is recorded on-chain. That design can reduce custodial dependence, but it also transfers more responsibility to the user. If a person approves a malicious transaction, exposes a recovery phrase, or installs a counterfeit extension, the protocol’s non-custodial architecture does not reverse the mistake.

Validator management therefore means more than selecting the highest displayed yield. It includes reviewing commission, uptime or voting performance where available, concentration concerns, operational reputation, and the practical process for changing or withdrawing a delegation. Reward figures are not fixed interest rates. They can vary as network conditions, validator economics, and the amount of actively staked SOL change. A validator with an attractive current return may still be a poor choice if the headline number hides unstable operations or an unusually high fee structure.

How dApp connectivity changes the security model

A decentralized application, or dApp, is a web interface that communicates with blockchain programs. When a Solana dApp connects to a browser wallet, the connection usually lets the application request the public wallet address and present transactions for approval. The dApp should not automatically receive the private key. The important security event occurs when the user signs a transaction, not merely when a website displays a “connected” status.

This is why visual familiarity can be misleading. A fraudulent website may imitate a legitimate staking dashboard, use convincing branding, and ask a user to approve an instruction that transfers assets rather than delegates them. The browser extension may faithfully show a request, but the user still has to inspect what is being authorized. Connection and authorization are different events; disconnecting from a site later does not necessarily undo a transaction that has already been confirmed.

For readers evaluating a browser-based Solana wallet, the practical discipline is simple but not trivial: install software only from a source you can independently verify, check the extension name and publisher carefully, keep the recovery phrase offline, and treat unexpected requests for that phrase as a decisive warning. Before approving a transaction, examine the recipient, program interaction, amount, and whether the action matches the stated purpose. When a site insists on urgency, guaranteed returns, or a “verification deposit,” skepticism is appropriate.

Users who want to examine how a Solana wallet extension is presented can review https://sites.google.com/walletcryptoextension.com/solflare-wallet-extension/. The link may help with product orientation, but it should not replace independent verification of the official installation path, permissions, and transaction behavior. In crypto, the safest interface is not necessarily the one with the most features; it is the one that makes the consequences of signing understandable.

Three ways to approach Solana staking

Direct delegation through a non-custodial wallet is the clearest option for users who want to choose validators themselves. It offers control over the wallet and, in principle, the ability to move or redelegate stake according to protocol rules. The trade-off is attention. The user must compare validators, understand activation and withdrawal timing, monitor changes, and avoid confusing a validator choice with a guaranteed return.

Liquid staking is a second approach. Instead of leaving the user with only a conventional delegated stake position, a liquid-staking protocol may issue a token intended to represent a claim on staked assets. That token can sometimes be used in other decentralized applications. The attraction is capital flexibility: the user may retain a form of tradability while seeking staking exposure. The cost is additional complexity. The user may face smart-contract risk, token liquidity risk, pricing deviations, protocol governance risk, and a more complicated exit process. Liquid staking is not simply “better staking”; it exchanges one set of constraints for another.

Custodial staking through an exchange or service is a third alternative. It can be easier for beginners because the provider handles validator selection and operational details. Yet the provider controls the relevant keys or account infrastructure, and the user depends on its security, policies, fees, regulatory posture, and withdrawal procedures. For US users, the legal and tax treatment of crypto activity can also depend on individual circumstances and may change over time, so a convenient interface should not be mistaken for personalized financial or tax advice.

These options cannot be ranked universally. Direct delegation tends to fit users who value control and are willing to learn. Liquid staking may fit users who understand the additional protocol layers and actually need liquidity. Custodial staking may fit someone who prioritizes simplicity and accepts counterparty dependence. The useful comparison is not “which pays the most?” but “which failure mode am I prepared to manage?”

Myths that make staking decisions worse

Myth: a browser extension is the validator. It is not. The extension is an access and signing layer. Validator operations occur through network infrastructure, while delegation is represented by on-chain instructions. If the extension disappears, the underlying on-chain state does not automatically vanish, although access to the wallet and the ability to sign future actions may become a practical problem.

Myth: the highest advertised APY is the best validator signal. A displayed rate is a snapshot or estimate, not a promise. Commission, performance, changing network issuance, and reward timing all matter. A lower apparent return from a reliable operator may be preferable to a higher figure that comes with operational uncertainty. Even this judgment remains imperfect because publicly visible metrics cannot reveal every future failure.

Myth: connecting to a dApp gives it control of the wallet. Connection generally exposes an address and enables transaction requests; signing authorizes an action. The distinction is important, but it does not make every connection harmless. A malicious application can still use persuasive prompts to induce an approval. Permission hygiene and transaction comprehension remain necessary.

Myth: staking makes SOL inaccessible forever. Staked positions can involve activation, deactivation, and withdrawal timing rather than instant liquidity. Exact behavior depends on the protocol and the wallet interface. Anyone who may need funds for rent, bills, taxes, or emergency expenses should not treat staked SOL as equivalent to cash in a checking account.

A practical framework for browser users

Before staking, write down the intended action in plain language: “delegate this amount of SOL to this validator,” for example. If the wallet prompt describes a different recipient, an unfamiliar program, or a transfer that does not fit that sentence, stop. This small translation test is valuable because it forces the human intention and the machine-readable transaction to meet in the same place.

Next, assess the validator independently from the wallet’s promotional presentation. Look for understandable information about commission, recent performance, identity or operating history where available, and how easily the stake can be changed. No single metric is sufficient. Also consider concentration: if many users select validators only because they appear first in a list, convenience can reinforce dependence on a small set of operators.

Finally, separate software security from investment judgment. A properly protected wallet can still hold an imprudent asset allocation, and a carefully selected validator cannot protect a recovery phrase stored in a cloud document. Use a dedicated browser profile or hardware wallet where appropriate, keep software updated, test with a small amount when learning, and maintain records of transactions. These measures reduce avoidable errors; they do not remove market volatility or protocol risk.

What to watch next

The meaningful direction for wallet extensions is not simply adding more buttons. It is improving transaction legibility: clearer program names, better explanations of staking states, more transparent validator comparisons, and warnings that distinguish a connection request from an asset transfer. If those features improve, browser staking could become easier without becoming falsely reassuring. The test will be whether users can understand what they are signing, not whether the interface looks modern.

The open question is how much validator selection should be automated. Ranking tools can help users navigate a crowded network, but automated defaults may concentrate stake or encode criteria that users cannot inspect. A future in which wallets recommend validators could be useful if the methodology is transparent and changeable. It could be harmful if convenience quietly becomes influence. For now, the strongest principle is modest: use the extension as a signing instrument, treat the validator as an independent operational counterparty, and make every delegation decision as though the displayed reward were uncertain.

FAQ

Can a Solana browser extension manage validator delegation?

It can provide the interface for creating, reviewing, and signing delegation-related transactions, depending on the wallet’s supported features. It does not operate the validator. The validator’s performance and the network’s staking rules remain separate from the extension.

Is connecting a wallet to a staking dApp safe?

Safety depends on the site, the requested transaction, and the user’s approval. A connection is not the same as signing, but a deceptive dApp can use a connection to present a harmful request. Verify the site, review the transaction carefully, and never disclose a recovery phrase to a website or extension prompt.

Should users choose direct staking, liquid staking, or custodial staking?

There is no universal best option. Direct staking offers more control but requires more responsibility. Liquid staking adds flexibility but introduces smart-contract and liquidity risks. Custodial staking is simpler but creates dependence on a service provider. The appropriate choice depends on which risks and operational duties the user understands and accepts.

MetaMask Wallet Download: What Ethereum Users Should Understand Before They Swap

The most dangerous misconception about downloading a crypto wallet is that the download itself creates security. It does not. A browser extension is only an interface: the real security boundary is the way keys are generated, stored, recovered, and used when a smart contract asks for permission. That distinction matters for anyone in the United States comparing a MetaMask wallet download with an exchange account or another self-custody tool. MetaMask is useful because it connects a wallet to decentralized applications, multiple networks, and trading routes. It is also unforgiving. If a user exposes a Secret Recovery Phrase or approves a malicious contract, a polished interface cannot reverse the loss.

For Ethereum users, the practical question is therefore not simply “Where can I download MetaMask?” It is “Which functions do I need, what risks am I accepting, and how will I verify every transaction?” MetaMask remains particularly strong as an Ethereum Virtual Machine, or EVM, wallet. It supports Ethereum and networks such as Base, Arbitrum, Optimism, Polygon, Linea, BNB Chain, Avalanche, and zkSync. But broader network coverage does not mean identical behavior everywhere. The same account label may conceal different address systems, fees, token standards, and recovery limitations.

MetaMask wallet logo representing a browser interface for controlling blockchain accounts and transaction permissions

What a MetaMask wallet actually controls

MetaMask is non-custodial. In practical terms, a centralized exchange normally controls the operational custody of assets while recording a user balance in its own system. MetaMask instead gives the user an interface for blockchain accounts whose signing authority is controlled by cryptographic keys. The wallet does not make Ethereum safer by itself; it makes signing, viewing balances, connecting to decentralized applications, and submitting transactions more accessible.

During wallet creation, the central recovery mechanism is a 12- or 24-word Secret Recovery Phrase. Anyone who obtains that phrase can generally recreate control of the associated wallet, while a user who loses it may have no institutional recovery desk to call. This is the first myth to correct: a password is not the same as the recovery phrase. A local password can protect access to the extension on one device, but it does not replace the underlying recovery material. The phrase should never be entered into a website, sent to support, photographed, or stored in an exposed cloud note.

MetaMask also supports hardware wallets such as Ledger and Trezor. This changes the key-management trade-off rather than eliminating risk. A hardware device can keep private keys in cold storage and require physical authorization, reducing the consequences of a compromised browser or computer. Yet users still need to verify the destination, network, contract interaction, and amount on the device and in the wallet. Hardware protection cannot make a deceptive transaction legitimate.

Why the official download path matters

A search for “MetaMask wallet download” can produce look-alike pages, sponsored results, cloned extensions, and phishing prompts. The educational value of a download guide is not merely convenience; it is helping the reader establish a chain of trust before any funds are moved. Use the project’s verified distribution channel, check that the extension is the expected product, and avoid installing files delivered through unsolicited messages. For readers who want a concise starting point for the metamask wallet extension, the same rule applies: treat any page as a starting point, then independently verify the extension and never disclose the Secret Recovery Phrase.

After installation, create a new wallet only in a private setting, record the recovery phrase offline, and test the setup with a small amount before attempting a large transfer. A test transaction does not prove that every future transaction is safe, but it can reveal a wrong network, an incorrect address format, or an unexpected fee. US users should also remember that wallet software is not automatically a tax record. Transaction histories, swaps, bridges, and token movements may need to be tracked separately for reporting purposes.

MetaMask Swap is a quote-selection mechanism, not a guarantee of the best trade

MetaMask Swap aggregates quotes from decentralized exchanges and uses routing logic intended to reduce slippage and manage gas costs. Slippage is the difference between the expected execution price and the price actually achieved as market conditions or available liquidity change. This aggregation can be useful because a user does not have to inspect every individual decentralized exchange manually. It does not mean the displayed quote is risk-free, final in every circumstance, or necessarily cheaper than every alternative at the moment of execution.

The hidden variable is execution quality. A route can be attractive on price but less attractive after network fees, price impact, approval transactions, and the possibility of failed execution are considered. On a congested network, gas can materially change the economics of a small swap. On a thinly traded token, a favorable headline price can coexist with substantial price impact. A careful user should compare the amount received, the network fee, the slippage setting, and the contract permissions being requested. “One-click” is a user-interface description, not a risk classification.

Token approvals deserve special attention. Many decentralized applications ask a wallet to authorize a contract to spend a token on the user’s behalf. An unlimited approval can remain active after a trade is complete. If the approved application is later compromised or the user interacted with a malicious contract, that permission may create a path to drain the approved asset. A safer mental model is to treat approvals like recurring access credentials: grant only what is necessary when possible, and review or revoke permissions that are no longer needed. A successful swap does not prove that every permission granted along the route is harmless.

Multichain reach creates convenience—and cognitive risk

MetaMask’s traditional strength is EVM compatibility. Ethereum users can move among supported networks while keeping familiar concepts such as addresses, gas, tokens, and smart contracts. Automatic token detection can display supported assets on major networks, and custom tokens can be imported using a contract address, symbol, and decimal count or through an integration offered by a block explorer such as Etherscan. The important limitation is that visibility is not the same as validation. A token appearing in a wallet does not establish that it is authentic, liquid, or valuable.

MetaMask has also expanded beyond EVM networks, including support for Bitcoin and Solana, with network-specific addresses generated for accounts. That expansion should not be interpreted as complete feature parity. Current limitations include the inability to import Ledger Solana accounts or private keys directly for Solana, as well as the lack of native support for custom Solana RPC URLs, with the wallet defaulting to Infura in that context. These boundaries matter to advanced users who depend on particular custody arrangements or infrastructure providers.

Snaps adds another layer. It is an extensibility framework through which developers can add functionality and support for non-EVM networks within the MetaMask environment. The benefit is a broader interface without requiring every feature to be built into the core wallet. The cost is another trust decision: users should evaluate what a Snap can access, what permissions it requests, and whether its developer and purpose are clear. An extensible wallet is not automatically a safer wallet; extensibility expands both capability and the surface that must be assessed.

An experimental Multichain API may allow applications to interact with several networks without requiring users to switch manually before each action. If this approach becomes dependable, it could reduce friction in multichain applications. It may also make network context less visible to users. That is a meaningful human-factors problem: removing one source of friction can also remove a cue that helped users notice where a transaction was occurring. The feature is best viewed as a signal to monitor, not as evidence that network-specific risks have disappeared.

How MetaMask compares with alternatives

Phantom is a natural comparison for users whose main activity is on Solana. Its advantage is specialization and a user experience shaped around that ecosystem. MetaMask may be preferable for users whose primary requirement is Ethereum and a wide EVM network set, especially when interacting with EVM-based decentralized applications. The trade-off is that a multichain MetaMask setup may involve more exceptions and uneven support than a wallet focused on one ecosystem.

Trust Wallet is often considered by users who want broad multichain coverage in a mobile-first environment. That breadth can be convenient for holding varied assets, but it can also make network, token, and application distinctions harder for beginners to track. Coinbase Wallet may appeal to US users who value a close relationship with the Coinbase exchange. The integration can simplify movement between exchange services and self-custody, but convenience should not be confused with the same custody model: an external exchange account and a self-custodied wallet remain different security arrangements.

A reusable decision rule is to choose the wallet around the dominant activity rather than the largest feature list. If Ethereum dApps and EVM networks are central, MetaMask is a coherent fit. If Solana is the primary environment, Phantom may reduce ecosystem friction. If broad mobile custody or exchange-linked workflows dominate, Trust Wallet or Coinbase Wallet may be more suitable. None removes the need to verify addresses, permissions, recovery procedures, and network selection.

What recent product messaging does—and does not—show

Recent MetaMask messaging describes a broader financial interface: buying and selling Bitcoin, Ethereum, and Solana, a money account with an advertised opportunity to earn up to 4%, global transfers, and a MetaMask Card with a stated reward of up to 3%. These are notable directions because they suggest a wallet becoming more than a browser-based signing tool. They also introduce additional questions about eligibility, fees, terms, counterparties, product jurisdiction, and whether a service is custodial or non-custodial.

Those questions are especially important in the US, where product availability and financial treatment can vary by state, service, and account type. Promotional percentages should be read as conditional terms rather than guaranteed returns, and card rewards should not be treated as an investment yield. The defensible conclusion is narrower: MetaMask appears to be pursuing a more integrated account experience. Whether that improves users’ outcomes depends on transparency, operational security, and whether the added convenience helps users understand transactions instead of encouraging automatic approval.

FAQ

Is MetaMask safe to download?

The extension can be a reasonable self-custody tool when obtained through a verified distribution channel and used with disciplined key management. Safety is not provided by the brand alone. Phishing sites, malicious dApps, exposed recovery phrases, misleading token contracts, and unlimited approvals remain material risks. Start with a small test transaction and keep significant long-term holdings in a hardware-wallet setup when appropriate.

Does MetaMask Swap always provide the cheapest price?

No. It aggregates routes and may improve convenience or execution, but the best outcome depends on liquidity, gas fees, price impact, slippage, approvals, and network conditions. Compare the final amount received and total transaction cost rather than relying only on the quoted exchange rate.

Can MetaMask replace every other crypto wallet?

No. It is especially well suited to Ethereum and EVM applications, while Phantom may be a better fit for Solana-focused activity, Trust Wallet for some broad multichain mobile workflows, and Coinbase Wallet for users prioritizing exchange integration. Network support and hardware-account limitations mean that no single interface should be assumed to provide identical custody and transaction behavior everywhere.

The sharpest way to evaluate a MetaMask wallet download is to separate interface convenience from control over money. MetaMask can connect Ethereum users to a large application ecosystem, aggregate swap routes, and increasingly span several networks. Its boundary is equally clear: the user remains responsible for recovery secrets, approvals, network context, and the meaning of each signature. That is not a flaw unique to MetaMask. It is the defining condition of self-custody—and the fact that should govern every click that follows.

Copati 34 anos de história!

O COPATI tem 34 anos de história dedicada a proteção do Rio Tibagi. Sua trajetória começa oficialmente em 21 de setembro de 1989, quando a situação do Rio Tibagi era bastante crítica, com danos significativos à fauna e flora de sua bacia hidrográfica. A população ribeirinha, que dependia da pesca, só conseguia capturar o peixe barbado. Era hora de discutir o repovoamento do rio. Os prefeitos de Ibiporã, José Maria Ferreira, e Jataizinho, Humberto Chamilleti, juntamente com representantes da antiga Secretaria Estadual de Recursos Hídricos e Meio Ambiente (SUREHMA) e da Universidade Estadual de Londrina (UEL), reuniram-se para discutir o assunto. Uma questão importante foi colocada pelos pesquisadores da universidade: por que os peixes do Tibagi estavam morrendo? Eles alertaram que repovoar o rio com peixes não bastava; era preciso identificar a causa do desaparecimento deles.

Paralelamente, no Brasil, surgiram iniciativas de consórcios de municípios para preservar bacias hidrográficas. O Superintendente da SUREHMA, Alberto Baccarim, buscou informações na experiência do movimento de recuperação do Rio Jacaré – Piepira, na região de Brotas, interior paulista, para ajudar a criar o COPATI. Na mesma época, encontrou o parceiro ideal para consolidar os planos: a empresa Klabin, que assinou com a SUREHMA um termo de compromisso para a instalação de equipamentos não poluentes e investimentos em projetos de recuperação do rio Tibagi. Assim nasceu o COPATI.